World Patient Safety Day 2026: Why Safe Care for Life Depends on Connecting the Dots

Every interaction within healthcare is a patient safety moment. For someone living with a long-term condition, those moments can extend across years of appointments, medications, tests, referrals, hospital admissions, discharge and ongoing care.

That is why World Patient Safety Day 2026, focuses on “Safe care for noncommunicable diseases”, under the slogan “Safe care for life!”

The World Health Organization (WHO) highlights the particular patient safety challenges associated with noncommunicable diseases (NCDs), including diabetes, cardiovascular diseases, cancers and chronic respiratory diseases. Because these conditions often require long-term treatment and repeated interactions with health systems, people living with NCDs can encounter safety risks across the entire continuum of care.

Globally, WHO estimates that 1 in 10 patients experiences harm during healthcare, with around half of that harm considered preventable. For people living with NCDs, long-term treatment needs, complex care and frequent interactions with health services can increase exposure to these risks over time.

But World Patient Safety Day also presents an opportunity to look beyond individual safety events.

When something goes wrong, can healthcare organisations connect what happened to what they already know? Can they learn from it? And can they demonstrate that learning has resulted in safer care?

For healthcare leaders, the challenge is not simply collecting more patient safety information. It is connecting the dots between reporting, learning and improvement.


One patient. Many safety moments.

Consider Sarah.

Sarah is 58 and lives with Type 2 diabetes and hypertension. Like millions of people living with long-term conditions, medications are an important part of managing her health.

During a routine medication round in hospital, a medication error occurs.

The error is identified and Sarah receives the appropriate care.

The immediate priority is, of course, Sarah's safety.

But from an organisational patient safety perspective, another important process is only beginning.

What happens next?

Is the medication error reported?

Is it investigated?

Can the organisation establish why it happened?

Have similar medication incidents occurred before?

Are corrective actions assigned?

Does a process or policy need to change?

And, crucially, can the organisation demonstrate that those actions resulted in improvement?

One medication error can represent many different patient safety moments.

How an organisation connects those moments can determine how much it learns from the event.


Medication safety demonstrates why connected patient safety matters

Medication safety is particularly relevant to World Patient Safety Day 2026.

WHO specifically identifies medication errors among the sources of harm that should be proactively addressed across NCD care. Its calls to action for health practitioners also emphasise reporting incidents, sharing good practices and contributing to a culture of continuous improvement.

For healthcare facility managers, WHO calls for organisations to establish a safety culture, promote incident reporting by health workers and patients, and use data and lived experience to drive improvement. That distinction is important.

Incident reporting is not the same as organisational learning.

Capturing the incident gives the organisation a valuable piece of information. But the value of that information depends on what happens afterwards.

If Sarah's medication error is reported but the report becomes another record sitting within a database, the organisation has captured what happened without necessarily reducing the likelihood of it happening again.

Effective patient safety management therefore needs to move beyond simply asking:

“Was the incident reported?”

It must also ask:

“What did we learn, what changed and did it make care safer?”

Reporting an incident should be the beginning, not the end

A strong incident reporting culture enables healthcare workers to raise concerns, report near misses and document adverse events without the process becoming centred on individual blame. That creates an opportunity to investigate the wider conditions surrounding an incident.

In Sarah's case, an investigation into a medication error might consider factors such as workflows, communication, staffing conditions, medication processes, clinical guidance or other contributing system factors.

The goal is not simply to establish who was involved. It is to understand why the system allowed the incident to happen.

That shift from individual blame towards systems learning is critical to building a stronger patient safety culture. But investigation itself is still only part of the process.

Once contributing factors have been identified, healthcare organisations need a reliable way to turn findings into action.

That might involve:

  • assigning corrective and preventive actions;

  • reviewing or updating a policy or procedure;

  • communicating changes to relevant teams;

  • providing additional education or training;

  • changing a workflow or process;

  • conducting follow-up audits; or

  • monitoring whether similar incidents continue to occur.

The patient safety loop is only truly closed when organisations can move from incident → investigation → action → evidence of improvement.
What if Sarah's incident isn't an isolated event?

Now imagine Sarah's medication error has been reported. On its own, the incident tells the organisation something important about Sarah's care. But what happens if three similar medication incidents were reported in another department?

What if patient feedback contains recurring concerns about medication information?

What if an audit has identified inconsistent compliance with a relevant procedure?

What if corrective actions relating to an earlier medication incident remain outstanding?

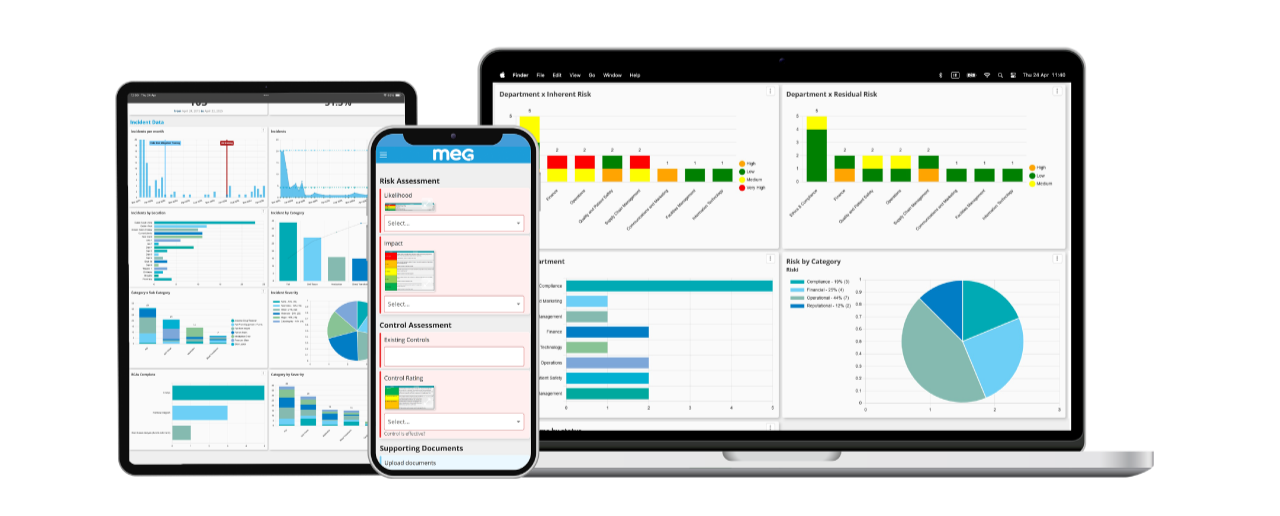
Individually, these may appear to be separate quality records. Together, they could represent something much more significant: an emerging patient safety signal.

This is one of the challenges facing healthcare quality and patient safety teams. Valuable information can exist across incident reports, near misses, patient feedback, complaints, audits, risk registers, policies and improvement actions.

When these activities are managed in isolation, seeing the bigger picture becomes harder. Connecting them allows organisations to move beyond individual events and ask more meaningful questions.

Are we seeing a pattern?

Where is risk increasing?

Have previous interventions worked?

Are the same contributing factors appearing repeatedly?

What are patients telling us that our other safety data isn't?

These are the questions that turn patient safety data into patient safety intelligence.

From patient safety data to patient safety intelligence

Healthcare organisations are not short of data. The challenge is making that data useful.

An organisation may have hundreds or thousands of incident reports, audit findings, complaints, feedback comments and improvement actions. Manually reviewing that volume of information and identifying meaningful connections can place a considerable burden on quality teams.

This is also where artificial intelligence can increasingly support patient safety and quality management. Within MEG, AI can help teams make sense of large volumes of quality information, including analysing patient feedback to identify themes that may warrant further investigation. AI should not replace clinical judgement, investigation or human decision-making.

Instead, AI can help healthcare teams surface the information that deserves their attention, making it easier to move from large volumes of safety data towards actionable insight. AI-powered analysis of patient feedback can help identify sentiment, recurring themes within the patient voice, providing another source of intelligence for quality improvement.

The objective is ultimately the same:

See the signal. Understand the risk. Act earlier.

Read our blog on AI sentiment analysis

Patient voice is part of the safety picture

Another central message of World Patient Safety Day 2026 is that people living with NCDs must be partners in safe care. WHO encourages healthcare organisations to use lived experience and data to improve care, while giving patients meaningful opportunities to raise concerns and contribute to safer systems.

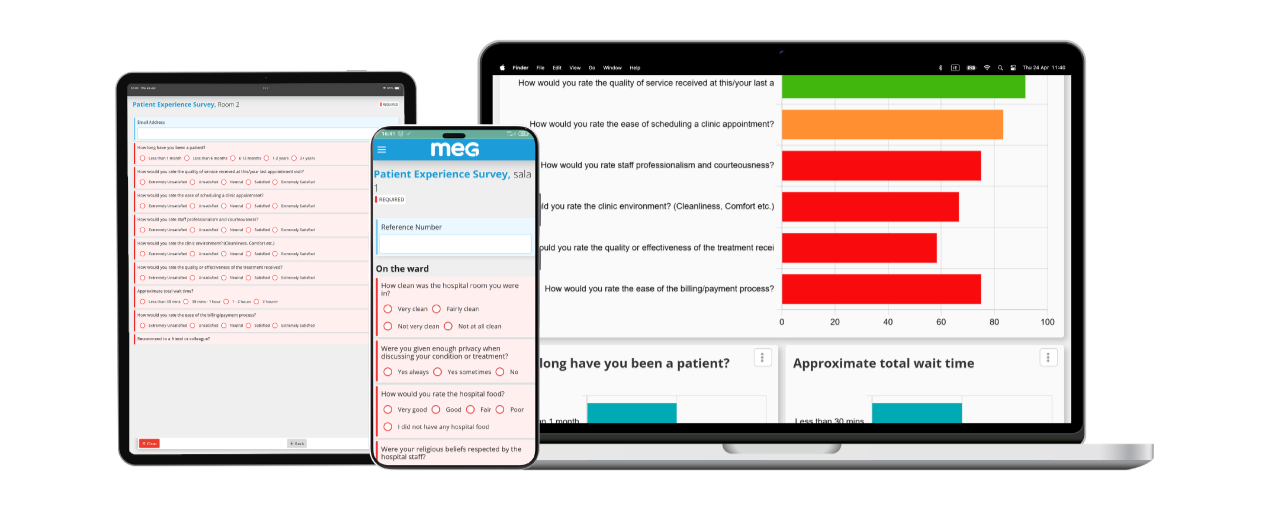
Patient feedback therefore shouldn't exist entirely separately from patient safety. A complaint about confusing medication information may initially appear to be an experience issue. One comment may be anecdotal. But repeated comments about the same issue, particularly when combined with incident or audit data, may indicate something that deserves closer attention.

Patient feedback can therefore provide an important additional perspective on risk.

Connecting the patient voice with other sources of quality and safety information helps organisations understand not just what their systems are reporting, but what patients are experiencing.
Closing the patient safety loop

For World Patient Safety Day 2026, WHO is calling on healthcare organisations to establish systems that enable safe NCD care, support health workers, promote incident reporting and use data and lived experience for continuous improvement.

Achieving that requires more than capturing information.

It requires a connected cycle of learning:

REPORT

Make it straightforward for staff to report incidents and near misses at the point of care.

INVESTIGATE

Understand what happened and identify the system factors that contributed.

CONNECT

Look beyond the individual incident for related risks, trends, previous incidents, patient feedback and quality findings.

ACT

Assign corrective actions, update processes and policies, and ensure responsibilities are clear.

MEASURE

Use audits, safety indicators and ongoing monitoring to establish whether interventions have worked.

LEARN

Share learning and use the evidence to drive continuous improvement.

Then repeat. Because patient safety isn't a project with an end date. It is a continuous organisational capability.

Safe care for life requires systems that learn for life

Sarah's medication error began as one patient safety event. But its potential impact doesn't have to end with Sarah. When an incident is reported, investigated and connected with other sources of safety information, it can create an opportunity for organisational learning.

When that learning leads to corrective action, updated processes and measurable improvement, one patient's experience can contribute to safer care for the next. That is ultimately what a mature patient safety system should enable.

Not simply more reporting.

More learning from what is reported.

Not simply more data.

Greater visibility of what the data is telling us.

And not simply responding to individual incidents.

Building safer systems as a result of them.

This World Patient Safety Day, the challenge for healthcare organisations is therefore not only to ask whether they have systems for capturing patient safety information.

It is to ask:

Are those systems connected well enough to turn information into learning, and learning into safer care?

At MEG, we believe healthcare quality and patient safety are strongest when the dots are connected. By bringing incident management, audits, patient feedback, policies and procedures, risk and improvement activity into a connected digital quality management environment, healthcare organisations can gain greater visibility across the patient safety journey and support a closed-loop approach to continuous improvement. Because safe care for life requires systems that learn for life.
MEG Named as a Supplier on the UK Government’s G-Cloud 15 Framework

MEG is a listed supplier on the UK Government’s G-Cloud 15 framework.

MEG is pleased to announce that we have been named as a supplier on the UK Government’s G-Cloud 15 framework, continuing our presence on one of the UK public sector’s key routes for procuring cloud technology.

Managed by the Government Commercial Agency (GCA), G-Cloud helps public sector organisations procure cloud-based hosting, software and support services through an established government framework.

For NHS organisations and other public sector healthcare providers, MEG’s inclusion provides a straightforward route to procure our cloud-based healthcare quality management software.

What does G-Cloud 15 mean for healthcare organisations? 

G-Cloud is designed to make purchasing cloud technology simpler for public sector organisations, giving buyers access to approved suppliers and cloud services through a recognised procurement route.

G-Cloud 15 introduces the most thorough supplier assessment in the framework’s history, with suppliers evaluated across areas including quality, technical proficiency and pricing.

For healthcare organisations evaluating MEG, our inclusion means they can procure MEG through a framework specifically designed to make accessing cloud technology across the public sector quicker and easier.

Supporting digital quality management across healthcare 

MEG helps healthcare organisations move away from paper-based, spreadsheet-driven and disconnected quality processes towards a secure, cloud-based approach to quality management.

From audits and compliance, to incident and risk management, document management, patient feedback and accreditation, MEG connects quality processes in one platform, helping teams improve visibility, accountability and continuous improvement.

Our inclusion on G-Cloud 15 makes it easier for eligible UK public sector organisations to access these capabilities through an established government procurement framework.

Looking Beyond the Obvious: Applying the Five Whys in Healthcare

When a quality issue is identified in healthcare, the first explanation is rarely the complete one.

A medication error occurs. A patient falls despite documented precautions. A deterioration in a patient's condition is recognised, but escalation is delayed. These events tell an organisation what happened, but the first explanation does not necessarily explain why it happened.

Too often, the immediate cause becomes the conclusion: someone selected the wrong medication, a procedure wasn't followed or information wasn't communicated. Corrective action may then focus on the individual rather than examining the conditions that allowed the incident to occur.

The Root Cause Analysis Five Whys technique helps healthcare organisations move beyond symptoms by encouraging teams to ask progressively deeper questions until they uncover the system, process or governance issues surrounding an event. 

Used appropriately, the Five Whys is less about finding someone responsible and more about asking a much more useful question: what allowed this incident to happen, and what needs to change to reduce the likelihood of it happening again? 

Looking Beyond the Obvious

The strength of the Five Whys lies in its simplicity. Rather than accepting the first explanation for an incident, investigators continue asking "Why?" to explore the factors that contributed to it. 

The goal isn't to ask exactly five questions. Some investigations reach the root cause after three questions, while others require six or seven. What matters is moving beyond immediate symptoms and understanding the systems, processes or organisational factors that contributed to the event.

This mindset is particularly important in healthcare.

Consider an investigation that concludes a medication error occurred because a member of staff "selected the wrong medication". That may be factually correct, but it leaves several important questions unanswered.

Why was it possible to select the wrong medication? Were similar products stored together? Were there previous near misses involving the same products? Did existing procedures recognise the risk? Were appropriate controls in place?

Those questions shift the investigation from who made the error towards why the system allowed the error to reach the patient.

Healthcare incidents can also involve multiple interacting factors, so Five Whys should not be treated as a way of forcing every event towards one definitive root cause. More complex incidents may require broader investigation methodologies. Instead, its value is in providing a structured way to challenge obvious explanations and explore underlying causes and contributing factors.

A Strong Five Whys Investigation Depends on Good Evidence 

Many organisations think of root cause analysis as something that begins after an incident. In reality, effective investigations depend on the quality of the information collected beforehand. 

Incident investigators may need to consider the original event report, the sequence and timing of events, accounts from the people involved, relevant clinical records, policies and procedures, previous similar incidents or near misses and other available quality and safety information. Audit findings can also provide useful supporting evidence where relevant. 

The Five Whys therefore shouldn't become an exercise in speculation. Each answer should encourage investigators to look for evidence that supports—or challenges—the emerging explanation.

applying the root cause analysis five whys in healthcare

A Five Whys Root Cause Analysis Example in Healthcare

Consider an illustrative scenario where a patient receives the wrong medication after two medicines with similar packaging are confused during administration. The error is identified after administration and the patient requires additional monitoring.  The immediate explanation might be that the wrong medication was selected.

A Five Whys investigation goes further.

Why did the patient receive the wrong medication?

Because the incorrect product was selected during medication administration.

Why was the incorrect product selected?

Because two medications with similar packaging were stored next to each other in the medication storage area.

Why were look-alike medications stored together?

Because the existing storage process did not require these medicines to be physically separated or clearly differentiated.

Why did the storage process not include additional controls for look-alike medications?

Because the risk associated with these products had not previously been identified within the medication storage procedure.

Why had the risk not been identified and incorporated into the procedure?

Because there was no established process for reviewing medication-related incidents and near misses to determine whether recurring risks required changes to storage controls and procedures.

The immediate cause of the incident was the selection of the wrong medication. Stopping there might lead to an individual member of staff receiving additional training or being reminded to check medications more carefully.

The Five Whys investigation reveals a wider issue. The organisation can now consider whether medication storage arrangements need to change, whether look-alike medicines should be separated or more clearly identified, whether the relevant procedure requires review and whether similar risks exist elsewhere.

This is an illustrative example. The causes, investigation methodology and appropriate controls following a medication incident will depend on the circumstances and the organisation's own patient safety processes.

The First "Why" May Lead to More Than One Answer

Real healthcare incidents are rarely as linear as a textbook Five Whys diagram. Imagine asking why escalation was delayed for a deteriorating patient. The investigation might identify several contributing factors: responsibilities were unclear during a shift handover, the escalation procedure was interpreted differently by different team members and competing clinical demands affected response times.

There isn't necessarily one chain of five questions leading neatly to one root cause. This is an important limitation of the technique.

Investigators need to remain open to multiple lines of enquiry rather than choosing the first plausible chain of answers. Five Whys can help teams explore an incident, but it shouldn't replace professional judgement or a more comprehensive investigation methodology where the complexity or severity of an event requires one.

Its simplicity is most valuable when it encourages deeper questioning, not when it oversimplifies a complex event.

From Investigation Findings to Action

Identifying contributing factors is not the end of an investigation. If an investigation identifies a weakness in medication storage, for example, the organisation needs to decide what controls should change, who is responsible for implementing them and how it will determine whether those changes have worked. Different findings may require different responses.

An outdated procedure may require formal review and controlled publication. A newly identified patient safety risk may need ongoing assessment and oversight. Changes to clinical practice may require specific actions with accountable owners. A targeted audit may then be appropriate to verify whether the agreed controls are being followed.

This is where the relationship between incident management and wider quality management becomes important. The Five Whys helps teams understand why an incident may have happened. The wider quality system provides the mechanisms for responding to what the investigation has uncovered.

Read our blog on turning safety events into lasting improvement

How MEG Connects Incident Investigations with Improvement 

Within MEG's Incident Reporting & Risk Management solution, healthcare organisations can manage reported incidents and the information associated with their investigation within a structured digital workflow.

But the investigation itself is only one part of the process. If findings identify a new or existing organisational risk, that risk can be managed and reviewed through risk management. If a policy or procedure contributed to the incident, the relevant documentation can be reviewed through MEG Docs, with version control and approval workflows helping organisations manage subsequent changes.

Corrective and improvement actions can also be assigned to named owners through MEG's built-in action plan feature, with target dates and progress tracked through to completion.

Hospital Risk Management: A Guide to Proactive Patient Safety

Effective hospital risk management is no longer just about responding to incidents after they occur. As healthcare becomes more complex, organisations need to identify and manage potential risks before they impact patient safety, staff wellbeing or operational performance.

From medication safety to regulatory compliance, hospitals face an increasing number of risks that require ongoing oversight. The challenge isn't simply recognising these risks, it's having the processes and tools in place to assess them consistently, monitor them over time and ensure appropriate action is taken.

Modern healthcare risk assessment software helps organisations move from reactive problem-solving to proactive risk management, giving governance teams greater visibility of organisational risk while supporting safer, more resilient healthcare systems.

In this guide, we'll explore the principles of effective hospital risk management, the role of a risk register and how integrated healthcare quality management software helps organisations strengthen governance and improve patient safety.

Hospital Risk Management Starts Before an Incident Occurs

Many people associate hospital risk management with investigating incidents after something has gone wrong. In reality, its greatest value lies in preventing those incidents from happening in the first place.

Risk management is the structured process of identifying potential hazards, assessing their likelihood and impact, implementing controls and reviewing them regularly to ensure they remain effective. Rather than asking "What went wrong?", effective organisations ask "What could go wrong, and what are we doing to prevent it?"

Potential risks exist across every area of healthcare, including:

  • Medication safety

  • Infection prevention and control

  • Clinical documentation

  • Workforce and staffing

  • Medical equipment

  • Information governance and cybersecurity

  • Patient flow and operational pressures


From Risks to Action: Building a Stronger Risk Management Process

Identifying risks is only the first step. Effective hospital risk management depends on having a structured process for assessing, monitoring and reviewing those risks over time.

This is where a real-time risk register becomes invaluable. Rather than acting as a static list of organisational concerns, a modern risk register should function as a live management tool that supports continuous improvement.

hospital risk management guide to proactive patient safety

Each identified risk should be assessed using a consistent methodology, assigned to an owner and regularly reviewed to ensure mitigation measures remain appropriate as circumstances change. Scheduled reviews help organisations maintain an accurate understanding of their current risk profile instead of relying on outdated assessments.

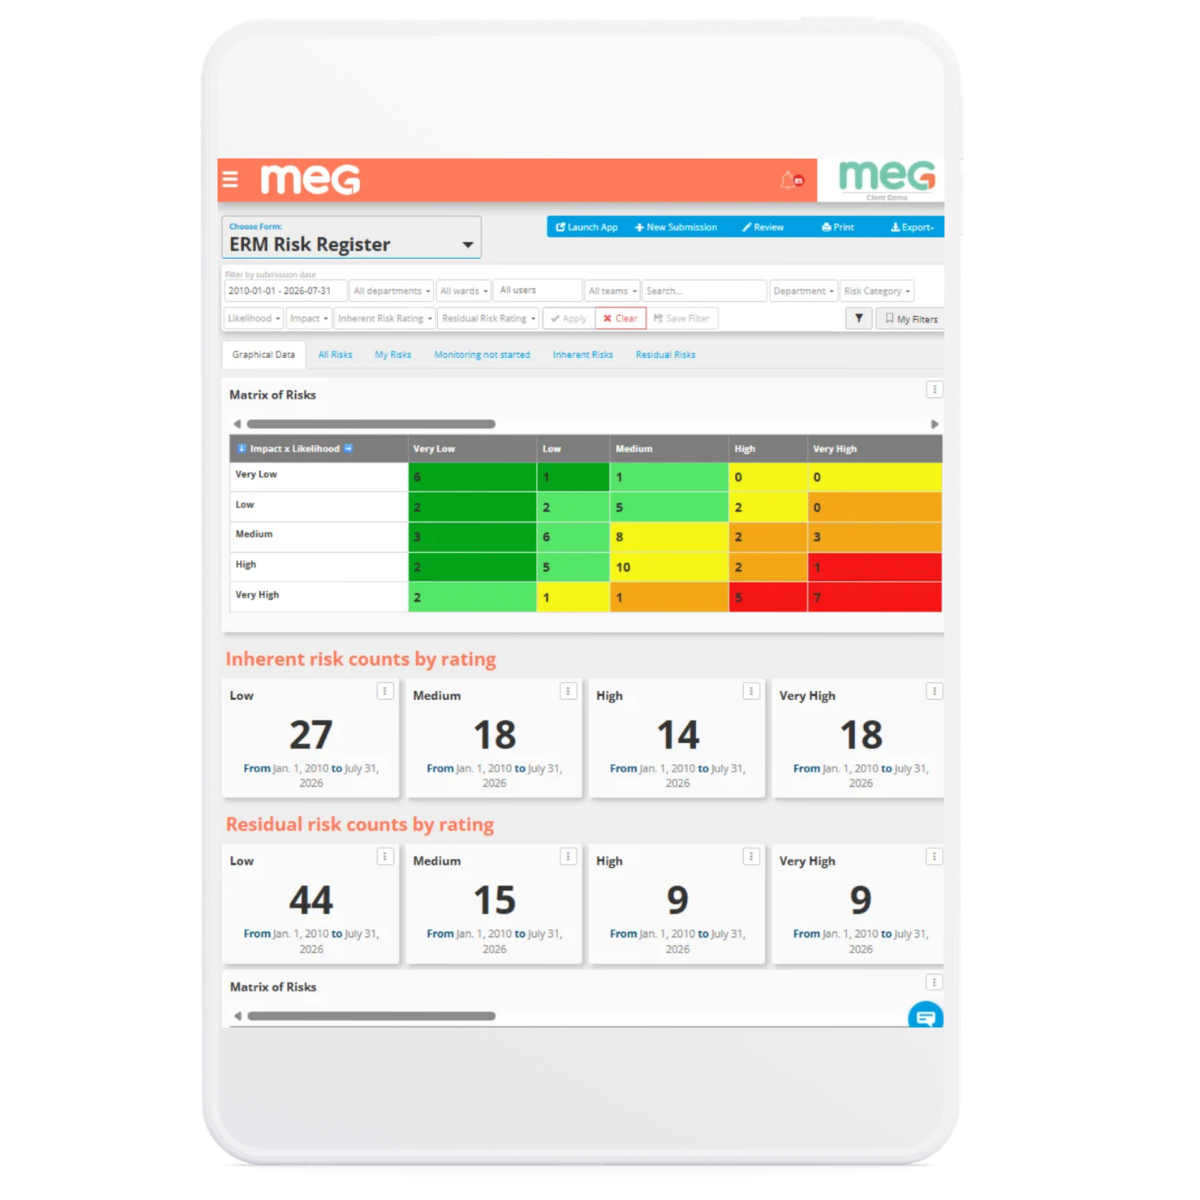
A widely adopted approach is the use of a 5×5 impact and likelihood matrix, which scores each risk based on its potential severity and probability. This enables governance teams to prioritise high-risk issues, allocate resources effectively and maintain greater oversight of organisational risk.

How Healthcare Risk Assessment Software Supports Better Decision-Making

Healthcare risk assessment software provides a more structured approach by standardising how risks are recorded, assessed and monitored. Automated workflows reduce administrative effort while making sure that changes to a risk's impact or likelihood trigger the appropriate notifications and follow-up activities.

Regular review schedules help teams keep track of risks rather than being forgotten after their initial assessment, while dashboards provide leadership teams with real-time visibility of organisational risk and emerging trends.

Ultimately, the goal of healthcare risk assessment software is not simply to digitise a risk register, but to provide governance teams with the information they need to make faster, more informed decisions that improve patient safety.


How MEG Helps Hospitals Manage Risk Proactively

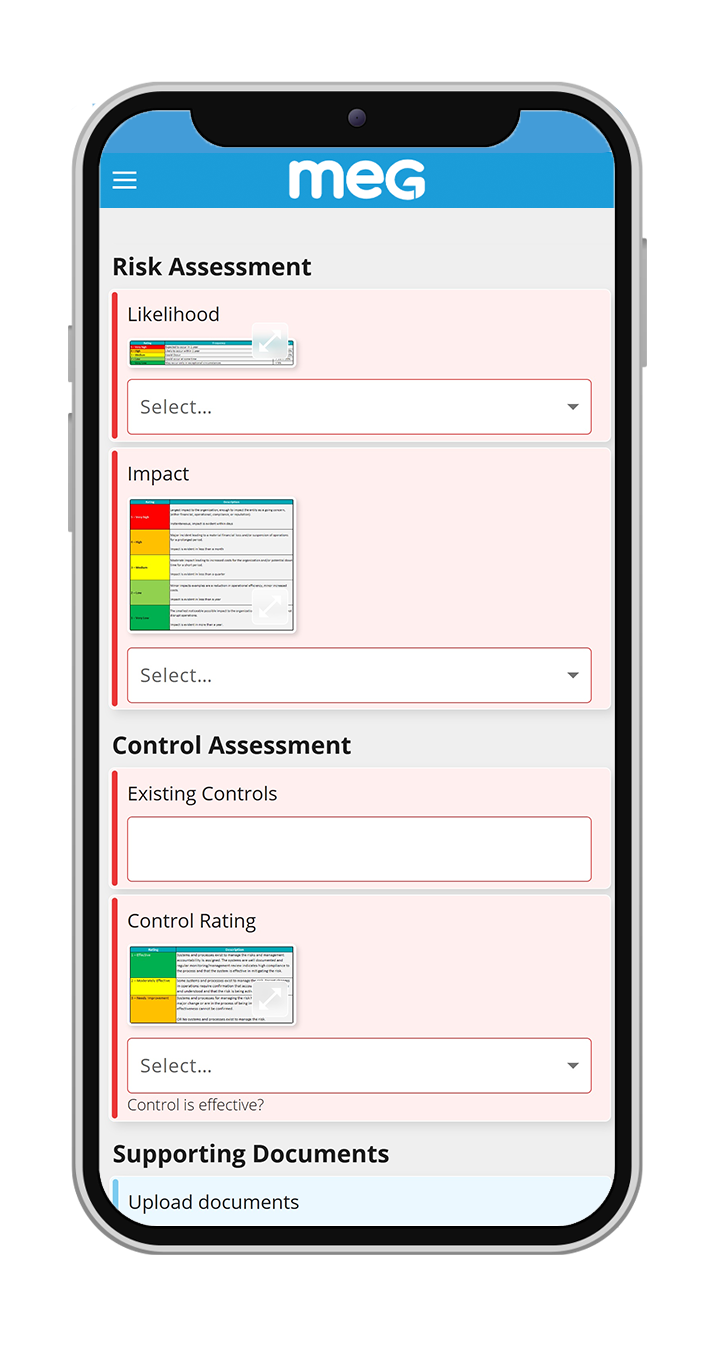
risk assessment form for hospital risk management

MEG's Incident Reporting & Risk Management solution is designed to help healthcare organisations move beyond reactive reporting and build a proactive approach to risk management.

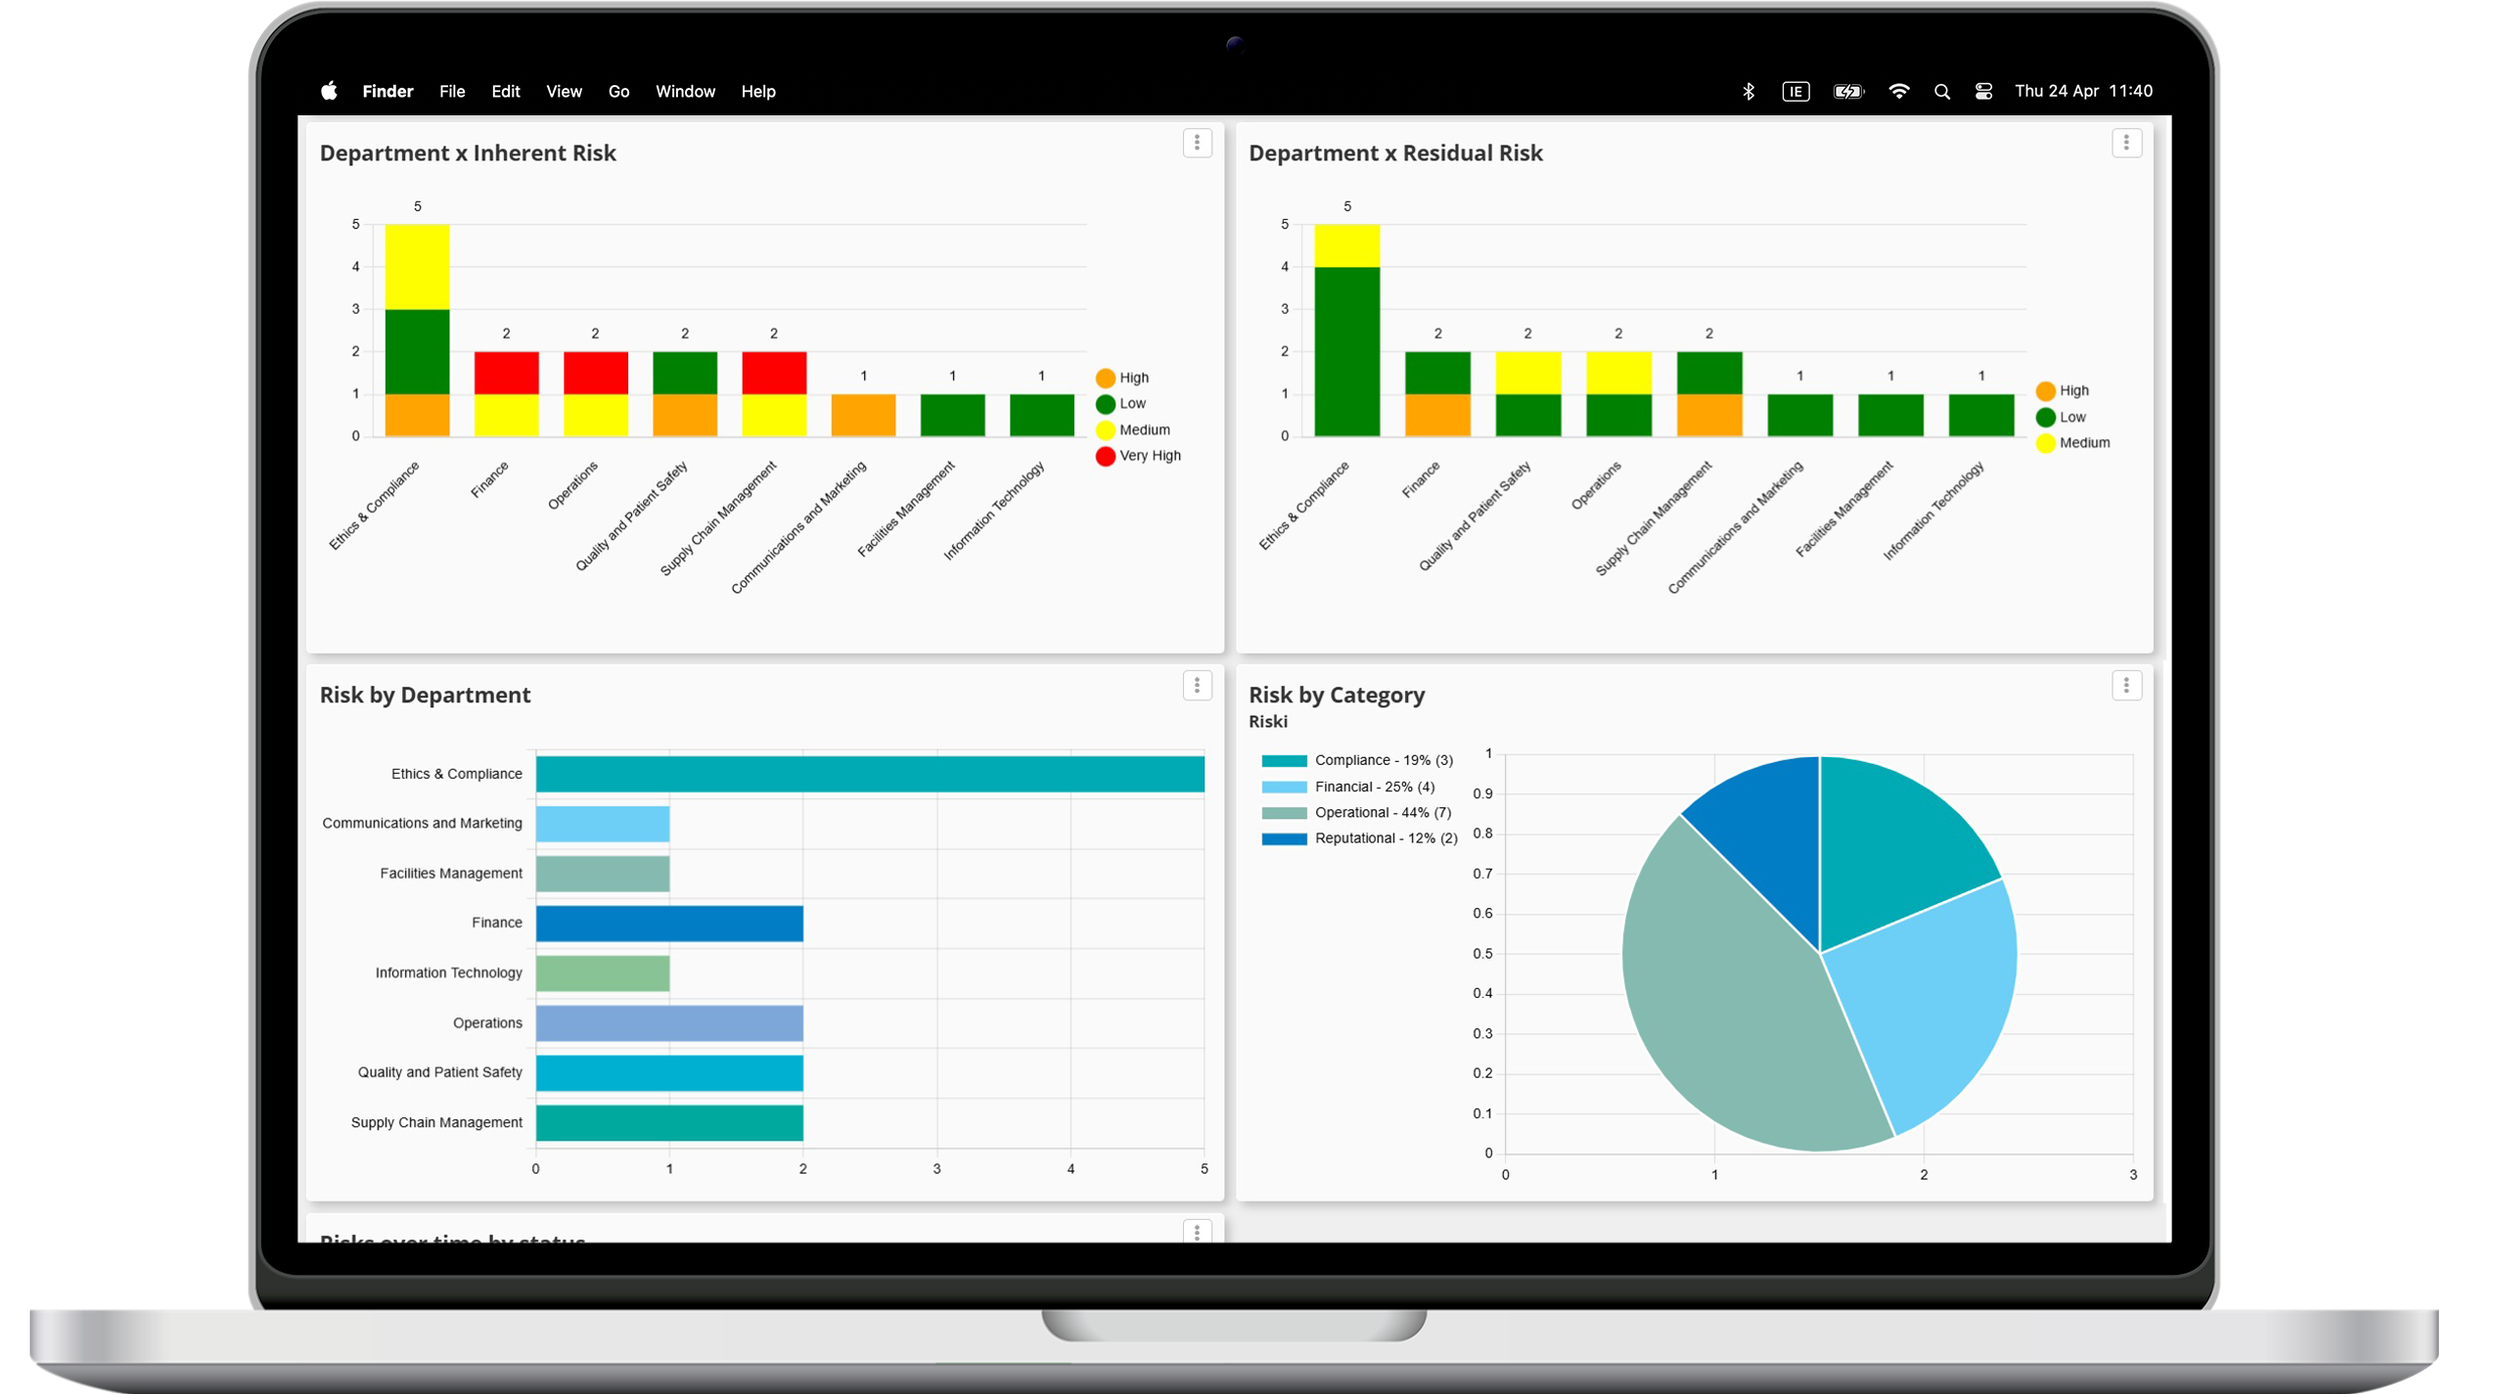
At the heart of the solution is a configurable Risk Register that enables organisations to identify, assess and monitor potential future hazards throughout their lifecycle. Risks are prioritised using a configurable 5×5 impact and likelihood matrix, making it easy for governance teams to identify high-priority risks and focus resources where they are needed most.

MEG also uses a risk tracker - which is a separate form used to keep track of risk behaviour over time, recording changes in impact and likelihood scores.

Unlike static risk registers, MEG supports scheduled reviews (e.g., monthly, quarterly) that automatically notify responsible users when a risk requires reassessment. This helps organisations keep their risk register current and helps maintain follow-up and compliance with risk management workflows. 

Workflow automation further strengthens governance by automatically triggering and saving changes in the risk tracker when risk scores are updated, reducing manual administration while improving consistency.

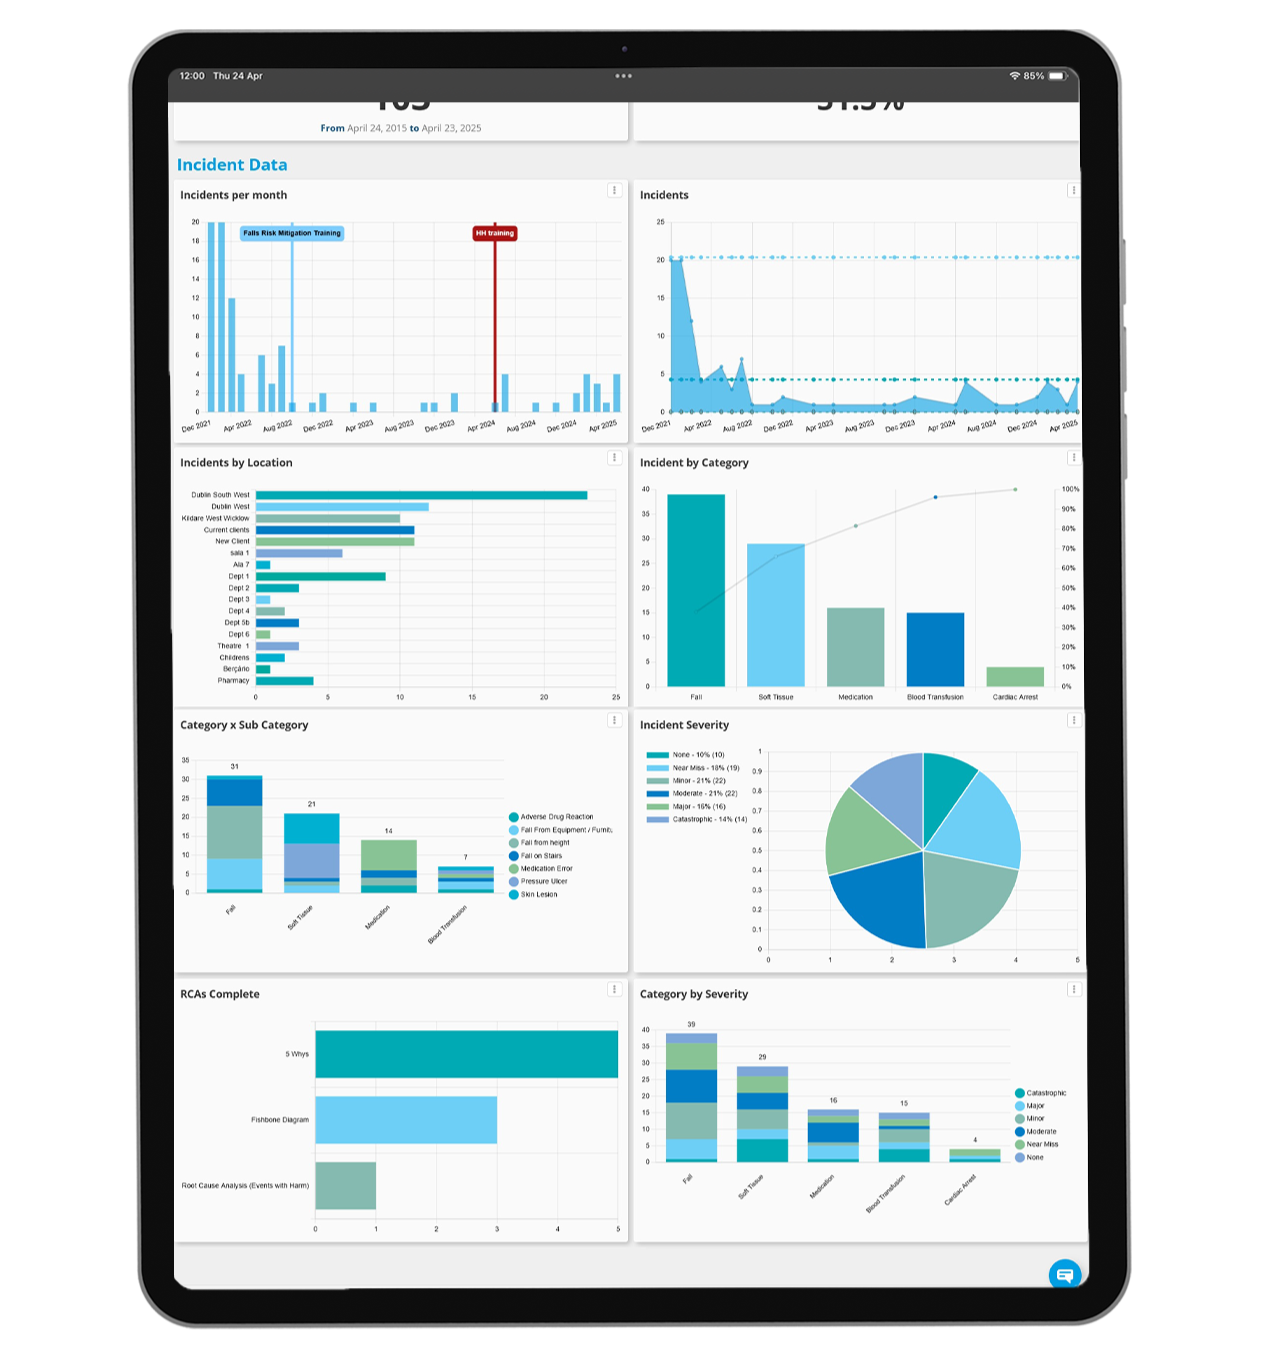
dashboard showing hospital risk management metrics

Risk management and incident reporting are often treated as separate processes, yet they are most effective when they work together.One of MEG's unique capabilities is that a risk can be escalated to an incident or vice-versa, with pre-populated data to avoid manual re-entry.

An incident represents something that has already happened, while a risk identifies the potential for future harm. In practice, the two are closely connected. A reported incident may uncover an underlying organisational risk that requires ongoing monitoring, while an existing risk may eventually materialise into an incident despite mitigation efforts.

Connecting these processes strengthens organisational learning and reduces duplication. Rather than creating new records from scratch, governance teams should be able to escalate an incident into a tracked organisational risk, or create an incident from an existing risk record, while retaining the information already captured.

An Integrated Approach to Healthcare Governance

Risk management delivers the greatest value when it is connected to the wider quality management system.

Within the MEG platform, identified risks can trigger audits to assess compliance, generate action plans to assign and monitor mitigation activities, or prompt updates to policies and procedures through Document Management. Where an identified risk develops into an adverse event, it can be linked directly to Incident Reporting, while trends emerging from Patient Experience and Patient Complaints can help identify new organisational risks before they escalate.

This integrated approach provides healthcare organisations with a single source of truth for governance, enabling quality, risk and patient safety teams to work from connected information rather than disconnected systems. The result is stronger oversight, improved accountability and a more effective framework for continuous quality improvement.


Conclusion

Effective hospital risk management is about more than maintaining a risk register, it is about creating a culture of continuous improvement where potential hazards are identified, assessed and managed before they affect patients, staff or organisational performance.

As healthcare organisations face increasing regulatory, operational and clinical complexity, integrated healthcare risk assessment software provides the visibility and structure needed to support proactive decision-making. By connecting risk management with incident reporting, audits, action plans, document management and patient feedback, organisations can strengthen governance while demonstrating a clear commitment to patient safety.

MEG Achieves Cyber Essentials Plus Certification

Trust is fundamental to healthcare technology. Whether managing incidents, policies, audits or patient feedback, healthcare organisations need confidence that the software they rely on is supported by robust cyber security practices.

We're proud to announce that MEG has achieved Cyber Essentials Plus certification, the highest level of assurance under the UK Government-backed Cyber Essentials scheme.

Unlike the standard Cyber Essentials certification, Cyber Essentials Plus requires an independent technical assessment of an organisation's cyber security controls. Rather than relying solely on a self-assessment questionnaire, certified organisations undergo testing to verify that key security measures are operating effectively in practice.

For MEG, this certification demonstrates our continued commitment to protecting the systems, information and services that support healthcare quality, compliance and clinical governance.

Going Beyond Self-Assessment

Cyber Essentials was introduced by the UK Government to help organisations protect themselves against the most common cyber threats. It establishes a recognised baseline of cyber security controls covering areas such as secure configuration, access control, malware protection, firewalls and software updates.

Cyber Essentials Plus builds on these requirements by adding an independent technical audit. Certified assessors test an organisation's environment to verify that these controls are not only documented but are also working effectively.

For organisations evaluating software providers, this additional level of verification provides greater assurance that cyber security controls have been independently validated.

Learn more about Cyber Essentials Plus on the official website

The Importance of Independent Security Assurance

Healthcare organisations operate in an environment where cyber resilience is essential. Patient information, operational continuity and regulatory compliance all depend on secure digital systems and trusted technology partners.

As procurement teams and governance leaders increasingly assess the cyber security posture of software vendors, independently verified certifications provide valuable evidence that security is embedded into organisational processes rather than simply documented in policy.

Cyber Essentials Plus helps demonstrate that an organisation's cyber security controls have been externally assessed against a recognised government-backed standard, giving customers additional confidence during supplier evaluation and procurement.

Cyber Essentials vs Cyber Essentials Plus 

While both certifications are based on the same five technical security controls, the level of assurance they provide is different. Cyber Essentials is achieved through a verified self-assessment, whereas Cyber Essentials Plus includes an independent technical assessment to validate that those controls are working effectively in practice.

Comparison Table: Cyber Essentials vs Cyber Essentials Plus

Comparison Table: Cyber Essentials vs Cyber Essentials Plus

For healthcare organisations assessing software suppliers, Cyber Essentials Plus offers an additional level of confidence because an independent assessor has verified the effectiveness of the organisation's cyber security controls, rather than relying solely on self-declared compliance. 

Cyber Essentials Plus complements the wider governance and security framework that underpins the MEG platform.

Alongside our existing certifications and attestations, including:

  • ISO/IEC 27001:2022 - Information Security Management Systems 

  • ISO/IEC 27017:2015 - Code of practice for information security controls for cloud services

  • ISO/IEC 27018:2019 - Code of practice for protection of personally identifiable information in public clouds

  • ISO/IEC 42001:2023 - Artificial Intelligence Management Systems

  • ISO 9001:2015 - Quality Management Systems

  • NHS Data Security and Protection Toolkit (DSPT)

  • SOC 2 Type II - System and Organization Controls 2, Type II 

Cyber Essentials Plus reinforces our ongoing commitment to protecting customer information while supporting healthcare organisations with a secure, reliable quality management platform.

Together, these certifications and attestations demonstrate that security, privacy and responsible AI governance are integrated into how MEG develops, delivers and continually improves its software.

View our certifications and attestations

What This Means for MEG Customers

For existing customers, Cyber Essentials Plus provides further independent assurance that MEG continues to invest in maintaining strong cyber security practices across its organisation.

For healthcare providers evaluating quality management software, it offers another layer of confidence that cyber security is taken seriously and independently assessed as part of our wider governance framework.

While no certification can eliminate cyber risk entirely, independent verification demonstrates an ongoing commitment to maintaining recognised security standards and continually strengthening organisational resilience.


Security Is a Continuous Commitment

Achieving Cyber Essentials Plus is an important milestone, but it is not an end point. Cyber security is an ongoing process of assessment, improvement and vigilance. As threats continue to evolve, so too must the controls, governance and processes that organisations use to protect their systems and data.

At MEG, we remain committed to continually strengthening our security posture while providing healthcare organisations with a trusted platform for quality, compliance and clinical governance.

Achieving Cyber Essentials Plus provides our customers with independent assurance that our security controls are not just documented, but effectively verified against robust, government-backed standards. This demonstrates our unwavering commitment to protecting the systems and patient data that our partners rely on. It’s an essential step in ensuring we remain a secure and dependable partner in healthcare quality and governance.
— Mark O’Reilly (Chief Information Officer, MEG)

Frequently Asked Questions

AI Sentiment Analysis in Healthcare: Turning Patient Feedback into Actionable Insights

ai sentiment analysis in healthcare

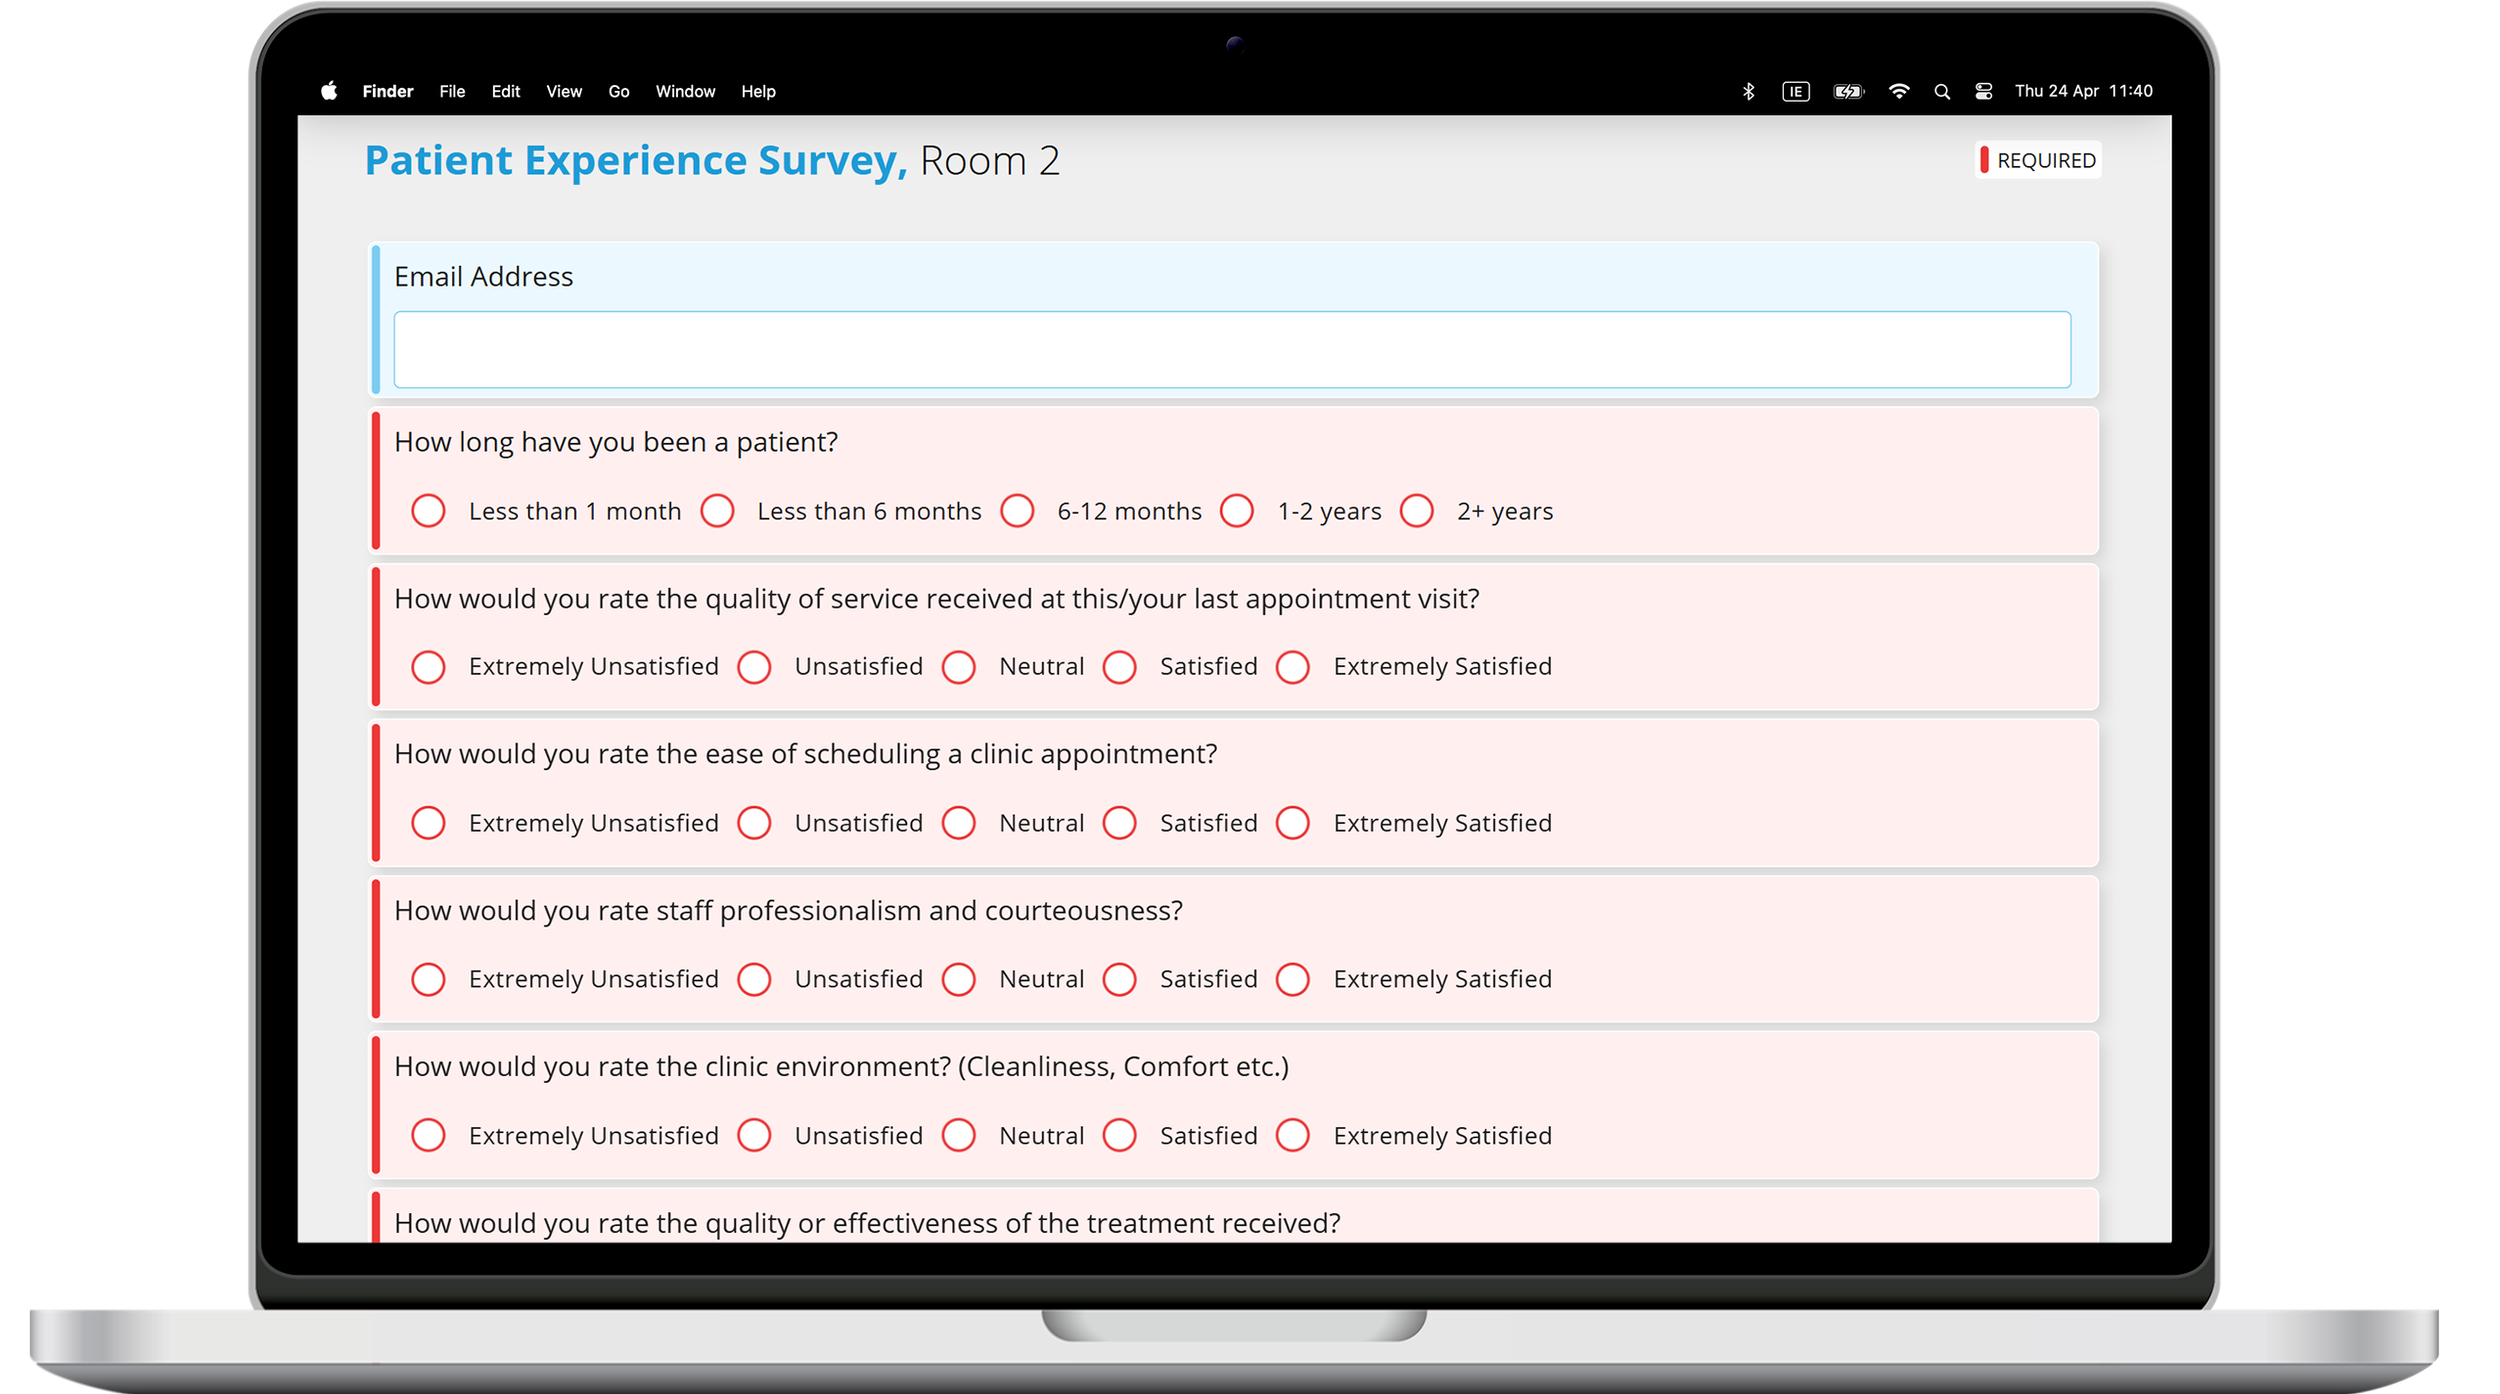
Healthcare organisations collect more patient feedback than ever before. Surveys, complaints, compliments, online forms, emails, voice recordings and free-text comments provide invaluable insight into patient experience. Yet for many organisations, the real challenge isn't collecting feedback, it's understanding it quickly enough to act.

A single patient comment may praise compassionate nursing care, raise concerns about the food, hospital cleanliness and poor communication during discharge all within the same response. Manually reviewing thousands of comments to identify themes, assign ownership and detect trends is time-consuming and increasingly unsustainable.

This is where artificial intelligence is transforming patient experience management in healthcare.

AI helps organisations analyse unstructured feedback at scale, identify emerging issues earlier and ensure the right teams receive the right information faster.

In this article, we'll explore how AI sentiment analysis and AI-powered insights are helping healthcare organisations move beyond simply collecting patient feedback to using it as a driver of continuous quality improvement.


Artificial Intelligence in Healthcare Is Moving Beyond Clinical Applications

When people think about artificial intelligence in healthcare, they often picture clinical decision support, diagnostic imaging or predictive analytics.

Yet some of the greatest opportunities for AI lie outside direct clinical care. Quality management and patient experience generate vast amounts of unstructured information that has traditionally required significant manual effort to review and interpret.

Patient feedback is one of the richest and often underused sources of organisational insight. Every comment represents an opportunity to understand what patients value, identify service gaps and improve care. However, without intelligent analysis, valuable insights can remain hidden within thousands of responses. This is where AI-powered insights deliver measurable value.

AI Sentiment Analysis Helps Organisations Understand Patient Experience Faster 

Sentiment analysis within MEG’s patient experience module uses artificial intelligence to determine the emotional tone behind written or spoken feedback.

Instead of simply identifying keywords, modern AI evaluates the context of the entire response to determine whether feedback is:

  • Positive

  • Negative

  • Mixed

  • Neutral

For healthcare organisations, this provides an immediate overview of how patients feel about the care they received. Rather than waiting for manual review, quality teams can quickly identify areas where patient experience may be deteriorating and prioritise responses accordingly. MEG enables healthcare organisations to change the categorisation based on their preference.

artificial intelligence in healthcare

One Comment Often Contains Multiple Stories

One of the limitations of traditional feedback analysis is treating every response as a single issue. In reality, patients frequently discuss multiple aspects of their experience within one comment.

For example:

"The nurses were fantastic, but I waited nearly two hours for my discharge paperwork and nobody explained the delay."

A manual reviewer might categorise this under "Discharge."

AI can identify multiple themes simultaneously, such as:

  • Nursing Care (Positive)

  • Communication (Negative)

  • Discharge Process (Negative)

  • Waiting Times (Negative)

This creates far richer organisational insight while ensuring each issue reaches the appropriate team for review.


AI-Powered Insights Enable Faster Action 

AI-powered insights help organisations:

  • Detect recurring themes across thousands of responses

  • Identify emerging service issues earlier

  • Surface positive patient experiences

  • Highlight departments requiring attention

  • Prioritise high-impact improvements

  • Support evidence-based quality initiatives

Instead of spending hours categorising comments, patient experience teams can focus on improving services.

Breaking Language Barriers with AI

Healthcare organisations serve increasingly diverse populations. Patient feedback may be submitted in multiple languages, making manual review more challenging. Modern AI can analyse sentiment across multiple languages, allowing organisations to understand patient experience regardless of the language used.

For multinational healthcare providers or organisations serving diverse communities, multilingual sentiment analysis provides a more complete picture of patient experience.

using artificial intelligence in healthcare to help with sentiment analysis

How MEG Uses Artificial Intelligence to Improve Patient Experience 

At MEG, we believe artificial intelligence should enhance the work of healthcare professionals. We also believe that healthcare AI should be governed responsibly. MEG is among the first healthcare quality management software providers to achieve ISO/IEC 42001:2023 certification, the world's first international standard for Artificial Intelligence Management Systems (AIMS). This independently verifies that our AI capabilities are developed and managed within a robust framework for governance, risk management, transparency and continuous improvement.

Our Patient Experience module uses AI to help organisations manage growing volumes of patient feedback more efficiently while ensuring valuable insights are not overlooked. MEG's AI capabilities include:

Intelligent Auto-Categorisation

Patient comments often contain multiple topics within a single response. MEG automatically identifies and categorises these themes, helping ensure each issue reaches the most appropriate team without requiring extensive manual review.

Context based AI Sentiment Analysis

MEG analyses feedback to identify whether patient sentiment is positive, negative, mixed or neutral. This provides organisations with an immediate understanding of overall patient experience while helping prioritise responses where attention may be needed most.

Multilingual Sentiment Detection

Patient feedback can be analysed across multiple languages, helping healthcare organisations understand experiences from diverse patient populations.

AI Voice Transcription

Voice notes can be automatically transcribed into text in multiple languages, making spoken feedback searchable, reportable and easier to analyse. Importantly, these AI capabilities support healthcare teams by reducing administrative workload while maintaining human oversight of decisions and follow-up actions.

Learn more: How MEG achieved ISO/IEC 42001 certification for responsible AI in healthcare.

When we designed the AI capabilities in the Patient Experience module, the goal was never to replace human judgement. It was to remove the bottleneck. Quality teams were spending hours categorising comments before they could even begin acting on them. Now the analysis happens in seconds, and their time goes into actually improving care.
— Mahmoud Assran (MEG Product Specialist)

AI Delivers Greater Value When Connected to Quality Improvement

Understanding patient feedback is only the first step.

Real improvement happens when insights lead to measurable action.

Within MEG's integrated Quality Management System, patient feedback can trigger wider quality improvement activities, including:

By connecting patient experience with governance, risk and quality management, organisations can demonstrate that patient feedback directly informs service improvement.

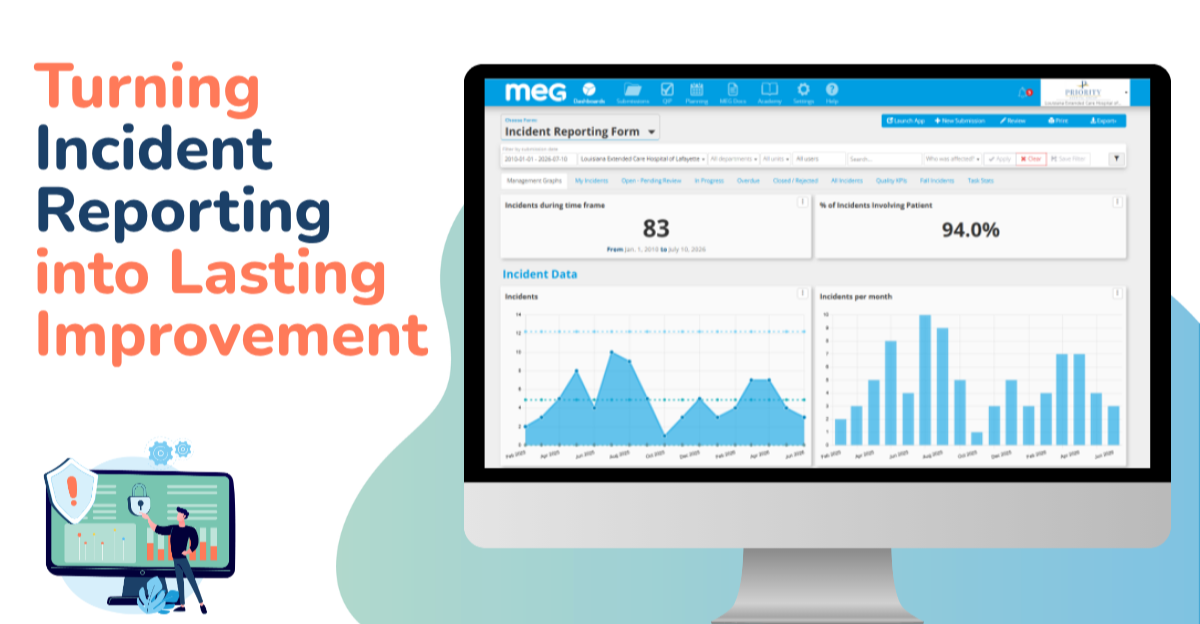
Hospital Incident Reporting: How Modern Healthcare Organisations Turn Safety Events into Lasting Improvement

hospital incident reporting

Patient safety doesn't improve because incidents are reported.

It improves because organisations learn from them, investigate their causes, implement corrective actions that tackle the systemic issues, and then monitor to ensure that the improvements stick.

Unfortunately, this is where many healthcare organisations struggle. Incident reports are often captured in one system, investigations managed elsewhere, actions tracked on spreadsheets and evidence stored across multiple locations. Valuable learning becomes fragmented, accountability is lost and the same risks continue to recur.

Modern healthcare incident reporting should do far more than record adverse events and near misses. It should provide healthcare organisations with a structured way to identify risk, support best practice in investigation of incidents, assign ownership of actions, demonstrate regulatory compliance and be able to track the impact on patient safety metrics.


Hospital Incident Reporting Is About More Than Capturing Events

Hospital incident reporting is the structured process of documenting patient safety events, near misses, adverse events, staff incidents and other situations that could affect the quality or safety of care.

However, effective incident reporting is not measured by the number of reports submitted. It is measured by what happens next. The purpose is not to assign blame but to build organisational learning.

Effective reporting allows healthcare providers to identify trends, investigate root causes, reduce future risk and improve patient outcomes. Organisations with mature reporting cultures treat incidents as opportunities to strengthen systems rather than identify individual fault. This aligns with international patient safety guidance, including WHO recommendations and the NHS Patient Safety Incident Response Framework (PSIRF), which emphasise learning and system improvement over blame.

What is an Incident in Healthcare? 

An incident is any event or circumstance that:

  • resulted in harm to a patient

  • had the potential to cause harm (near miss)

  • affected staff safety

  • disrupted clinical operations

  • compromised regulatory compliance

  • created organisational risk

Examples include:

  • Medication errors

  • Patient falls

  • Pressure injuries

  • Equipment failures

  • Patient identification errors

  • Violence and aggression

  • Data breaches

  • Clinical documentation errors

  • Security incidents

  • Occupational injuries

Capturing both adverse events and near misses is essential because near misses often reveal weaknesses before patients are harmed.


Why Incident Reporting Matters in Hospitals 

Healthcare is one of the most complex operational environments in the world. Every day, thousands of clinical decisions, handovers, procedures and communications occur across multiple departments. Even well-designed systems can experience failures. Without structured incident reporting, organisations lose visibility of emerging risks.

An effective incident reporting system enables hospitals to:

  • Detect patient safety risks earlier

  • Identify recurring themes and trends

  • Support root cause analysis

  • Meet accreditation and regulatory requirements

  • Improve organisational learning

  • Strengthen governance

  • Increase accountability

  • Demonstrate continuous quality improvement

Research and international patient safety guidance consistently highlight incident reporting as a critical component of organisational learning, while also recognising that reporting alone is insufficient unless organisations act on the findings.


Reporting Incidents in Healthcare Isn't Enough 

One of the biggest misconceptions is that reporting an incident improves safety. It doesn't. Reporting simply creates information.

Real improvement happens when organisations:

  1. Investigate what happened

  2. Understand why it happened

  3. Identify root causes

  4. Assign corrective actions

  5. Monitor progress

  6. Verify effectiveness

  7. Share organisational learning

This "closed-loop" approach is increasingly expected by regulators and accreditation bodies because it demonstrates that healthcare organisations are learning from incidents rather than simply documenting them. JCI and PSIRF, for example, place strong emphasis on learning, proportionate response and safety improvement following incidents.

Characteristics of an Effective Incident Reporting System in Hospitals

Not all incident reporting systems deliver meaningful improvement. The most effective systems combine usability with governance and analytics.

Key capabilities include:

Simple Reporting

Staff should be able to submit incidents quickly from desktop or mobile devices using intuitive forms.Complicated reporting processes discourage reporting.

Standardised Workflows

Consistent categorisation ensures data quality and makes trend analysis more reliable across departments and sites.

Immediate Notifications

Appropriate stakeholders should automatically receive alerts when serious incidents are reported.

Investigation Management

Investigations should be documented within the same system, including timelines, evidence and findings.

Root Cause Analysis

The system should support structured investigation methodologies rather than relying solely on narrative descriptions.

Action Management

Every recommendation should become a tracked action with:

  • ownership

  • deadlines

  • escalation

  • completion monitoring

Analytics and Dashboards

Healthcare leaders need real-time visibility into:

  • incident volumes

  • severity

  • recurring themes

  • overdue actions

  • departmental performance

  • organisational risk

Regulatory Reporting

Evidence should be readily available for inspections, accreditation surveys and governance meetings.

Building a Strong Incident Reporting Culture 

Technology alone cannot create safer healthcare. Organisational culture plays an equally important role.

Hospitals with high reporting rates are not necessarily less safe.

In many cases, they are safer because staff feel confident reporting issues without fear of blame.

High-performing organisations typically:

  • encourage near miss reporting

  • provide timely feedback to reporters

  • communicate lessons learned

  • recognise improvement opportunities

  • involve frontline staff in solutions

  • demonstrate visible leadership commitment

How MEG Helps Hospitals Close the Loop 

At MEG, we believe incident reporting should be the starting point not the end point of continuous improvement.

Our healthcare quality management software connects incident reporting with every stage of the quality improvement process, helping hospitals move from identifying risks to demonstrating measurable outcomes.

With MEG, organisations can:

  • Capture incidents from anywhere across the organisation

  • Manage investigations and root cause analysis

  • Generate corrective action plans

  • Track progress within the software

  • Monitor overdue actions and accountability

  • Identify trends through real-time dashboards

  • Produce evidence for inspections and accreditation

  • Demonstrate continuous quality improvement

Unlike standalone incident reporting software, MEG integrates incident management with the wider healthcare governance ecosystem.

For example, an incident can trigger:

  • an Audit to verify compliance across departments

  • an Action Plan to assign, monitor and verify corrective actions

  • updates to Policies and Documents to reflect new procedures

  • a Patient Experience review where complaints or feedback relate to the same issue

  • accreditation evidence showing how risks were identified, addressed and monitored over time

Ready to modernise your hospital incident reporting process? 

Discover how MEG's integrated Healthcare Incident Reporting & Risk Management solution helps hospitals capture incidents, investigate causes, track actions and demonstrate continuous quality improvement.

MEG Achieves ISO 42001 Certification, Joining the Small Group of HealthTech Companies with Responsible AI.

MEG ISO 42001:2023 certification badge issued by Citation ISO Certification for Artificial Intelligence Management

MEG's ISO/IEC 42001:2023 certification, issued by Citation ISO Certification — the international standard for Artificial Intelligence Management Systems. MEG achieved certification with 17 positive observations and zero nonconformances.

As a quality management software provider built exclusively for healthcare organisations, MEG has always believed that technology used in clinical governance, compliance, and patient safety must be held to the highest standard. That belief does not stop at our quality management software - it extends to how we build, govern, and deploy Artificial Intelligence features that power it.


That is why we are proud to announce that MEG has achieved ISO/IEC 42001:2023 certification - the international standard for AI Management Systems. Our audit was completed with 17 positive observations and zero nonconformances, a result that reflects the depth of work our team has put into building responsible AI governance from the ground up.


What ISO 42001 Certification Means for AI Governance in Healthcare

ISO/IEC 42001:2003 is the world's first internationally recognised, certifiable standard for AI management systems. Published in December 2023, it provides a structured framework for organisations that develop, provide, or use AI systems, setting out requirements for how AI should be governed, monitored, and continuously improved.

In practical terms, certification means an independent third party has verified that MEG has the policies, processes, and controls in place to manage AI responsibly across the full lifecycle; from how risks are identified and mitigated, to how decisions made by AI systems are documented, reviewed, and accountable.

The standard addresses some of the most pressing concerns around AI in regulated industries: transparency, bias, ethical use, data governance, and human oversight. It's designed not just as a compliance exercise, but as an operational framework that embeds responsible AI into how an organisation actually works, using the ‘Plan-Do-Check-Act’ methodology familiar from other ISO management system standards.

For healthcare organisations, AI management systems provide a structured approach to governing AI safely and consistently. As AI becomes increasingly embedded in clinical, operational, and quality processes, AI management systems in healthcare help organisations establish clear accountability, manage risks, and demonstrate that AI is being developed and used responsibly. ISO 42001 certification provides an internationally recognised framework for achieving this.

MEG was independently assessed and approved by Citation ISO Certification Limited.

Why AI Management Systems Matter in Healthcare

Healthcare is one of the most AI-sensitive environments in the world. Decisions informed by technology can affect patient safety, clinical outcomes, and organisational accountability. The stakes for getting AI governance wrong are not abstract.

For quality managers, compliance officers, and clinical governance leads, AI governance in healthcare is becoming a practical assurance question. When AI is embedded into operational systems, organisations need confidence that vendors can demonstrate transparency, oversight, risk management, and accountability.

For MEG's customers: quality and compliance teams in hospitals, health systems, and regulated healthcare organisations, the question of whether their software vendor governs AI responsibly is increasingly not a nice-to-have. It is a procurement consideration, a governance question, and in many cases, a trust issue. ISO 42001 certification gives our customers a clear, independently verified answer: Yes! MEG has a structured, audited system in place for responsible AI.


A Rare Distinction

While awareness of ISO/IEC 42001:2003 is growing rapidly, adoption remains limited. As of mid-2026, it is estimated that between 350 and 500 organisations worldwide have achieved this certification. For context, there are thousands of organisations globally holding ISO 27001 (information security) certification.

We are proud to be among this early group and to be one of the few healthtech companies to have achieved it. In a sector where trust is everything, we think that distinction matters.


What ISO 42001 Certification Means for MEG Customers

For existing MEG customers, this certification reinforces what you already know about how we work: with rigour, with transparency, and with your regulatory environment firmly in mind.

For organisations evaluating quality management software, it is a signal worth taking seriously. ISO 42001 certification gives healthcare organisations a clear signal: MEG’s quality management system has been independently assessed against an internationally recognised framework for responsible AI. As AI becomes more deeply embedded in the tools healthcare teams use every day, the governance behind those tools matters as much as the features.

We are committed to maintaining and building on this certification as our AI capabilities grow - and as the regulatory landscape around AI in healthcare continues to evolve.

At MEG, we have treated AI governance and ethics as enablers of innovation, not obstacles to it, from the outset. By embedding this principle, we have built a strong AI foundation for responsible growth. Achieving ISO 42001 certification validates this approach in practice. This is just the beginning, and we will continue building on this foundation.
— Guvanch Meredov - Head of Compliance and Certified AI Governance Professional, MEG

FAQ’s

Celebrating 10 Years of MEG and the Team Behind the Journey

On 6th May 2016, MEG officially began its journey in Dublin’s Digital Hub (still our home today), with a simple but ambitious mission – to make life easier for frontline healthcare workers, and safer for patients.

Before founding MEG, CEO Kerrill Thornhill, spent more than 10 years building software across different industries, but healthcare always stood out to him, not just because of its complexity, but because of the people working within it. He recognised the opportunity technology had to make a real difference on the frontline.

There is no more complex environment than healthcare. Building apps and systems for healthcare workers was something I always really loved doing.
— Kerrill Thornhill, CEO & Founder

As part of our 10-year celebrations, we sat down with some of the original MEG team members, who still work at MEG, to reflect on those early days, the milestones that shaped the company, and where they see MEG heading next. You can see the full interview here:

A Look Back at Some Big Moments Along the Way

2016 – The Early Days of MEG

MEG officially landed some of its very first healthcare customers close to home, including Beaumont Hospital in Ireland and Guy’s & St Thomas’ NHS Foundation Trust in the UK. Looking back 10 years later, we are incredibly proud to still work closely with both organisations today.

The early MEG team remember those years as busy, exciting and full of learning. Kerrill spent countless hours travelling to hospitals across Ireland and the UK, listening to frontline staff, gathering feedback and continuously improving the platform together with the people using it every day.

We would give hospitals early versions of our app, they would give feedback on how to improve it. There was a lot of back and forward, product iteration and really fast development.
— Peter Clifford, COO

2017 – Launching Our Very First Audit App

In 2017, MEG launched its Audit App on iOS and Android, helping healthcare teams move away from paper-based auditing and making audits easier, faster and more accessible. Later that year, we were thrilled to see our Audit App win the Net Visionary Award for Best Mobile App for Fast Moving Businesses. For a young healthcare technology company still in its early days, it felt like a huge moment and an exciting sign of what was possible. 

2018 – Building technology around frontline experiences

In 2018, MEG launched the Campus Guide App for St James’s Hospital in Dublin, another exciting step forward in using technology to solve practical everyday healthcare challenges and improve everyday experiences for staff and patients.

 Behind the scenes, the team was also working closely with more and more healthcare organisations, strengthening relationships, listening to frontline feedback and continuing to shape the platform around the real needs of staff and patients.

2019 – A Turning Point in the MEG Journey

2019 became one of the biggest turning points in MEG’s journey. 

That year, MEG joined the NDRC Accelerator Programme, which brought not only funding, but also invaluable guidance and support at a really important stage of growth

Through the programme, the team refined MEG’s marketing message, strengthened its go-to-market strategy and, most importantly, found real product-market fit. 

We realised that what we were actually doing was more than digitising audits, it was improving quality and patient safety. That changed everything for us. We shifted our focus, redeveloped our website and built the product specifically around healthcare quality and patient safety. It also helped shape the company’s first investor deck, which later supported investment and the growth of the team that would take MEG to the next stage.

2020 - Expanding into Asia-Pacific

In 2020, the world changed almost overnight as COVID-19 spread rapidly across the globe.

 Healthcare systems came under enormous pressure and frontline healthcare workers faced challenges unlike anything seen before. During this time, healthcare organisations accelerated digital transformation at speed, and the demand for connected quality and governance platforms grew rapidly

This period created new opportunities for MEG to support healthcare organisations internationally. During this period  we expanded into Asia-Pacific, marking another major milestone in MEG’s growing global journey.

2021 – Growing across new regions and new teams 

In 2021, MEG continued its global expansion into the Middle East and Latin America 

It was an exciting period of growth, not just geographically, but also as a team. As MEG expanded into new regions, the team also continued growing internationally to better support healthcare organisations across different healthcare systems, languages and cultures.

2022 – Celebrating the Impact Healthcare Teams Achieved with MEG

2022 brought a particularly proud moment for the MEG team, as one of our valued customers, St Vincent’s Private Hospital, won the VTE Award using MEG’s Audit Tool

Moments like these have always meant a lot to the team because they reflect something much bigger than software. They represent the real impact healthcare teams can achieve when they have the right tools, support and processes around them.

2023 – More People, More Ideas and More Momentum 

By 2023, MEG continued to grow both as a team and as a platform. 

As more healthcare organisations came on board globally, the team expanded across different regions, bringing together people with a wide range of experience, languages and expertise. 

At the same time, the platform itself continued evolving with new modules, features and functionality added to support the growing quality, patient safety and governance needs. 

We solve their main problems and we actually grow along the way, along with the customers.
— Anna Gularska, Technical Sales Support Manager

2024 – Entering the US Market

In 2024, MEG entered the US market, marking a major milestone in our global journey. 

During this time, we began working with DMC Primary Care and Priority Hospital Group, bringing MEG’s end-to-end Quality Management Platform into one of the world’s largest and most complex healthcare markets.

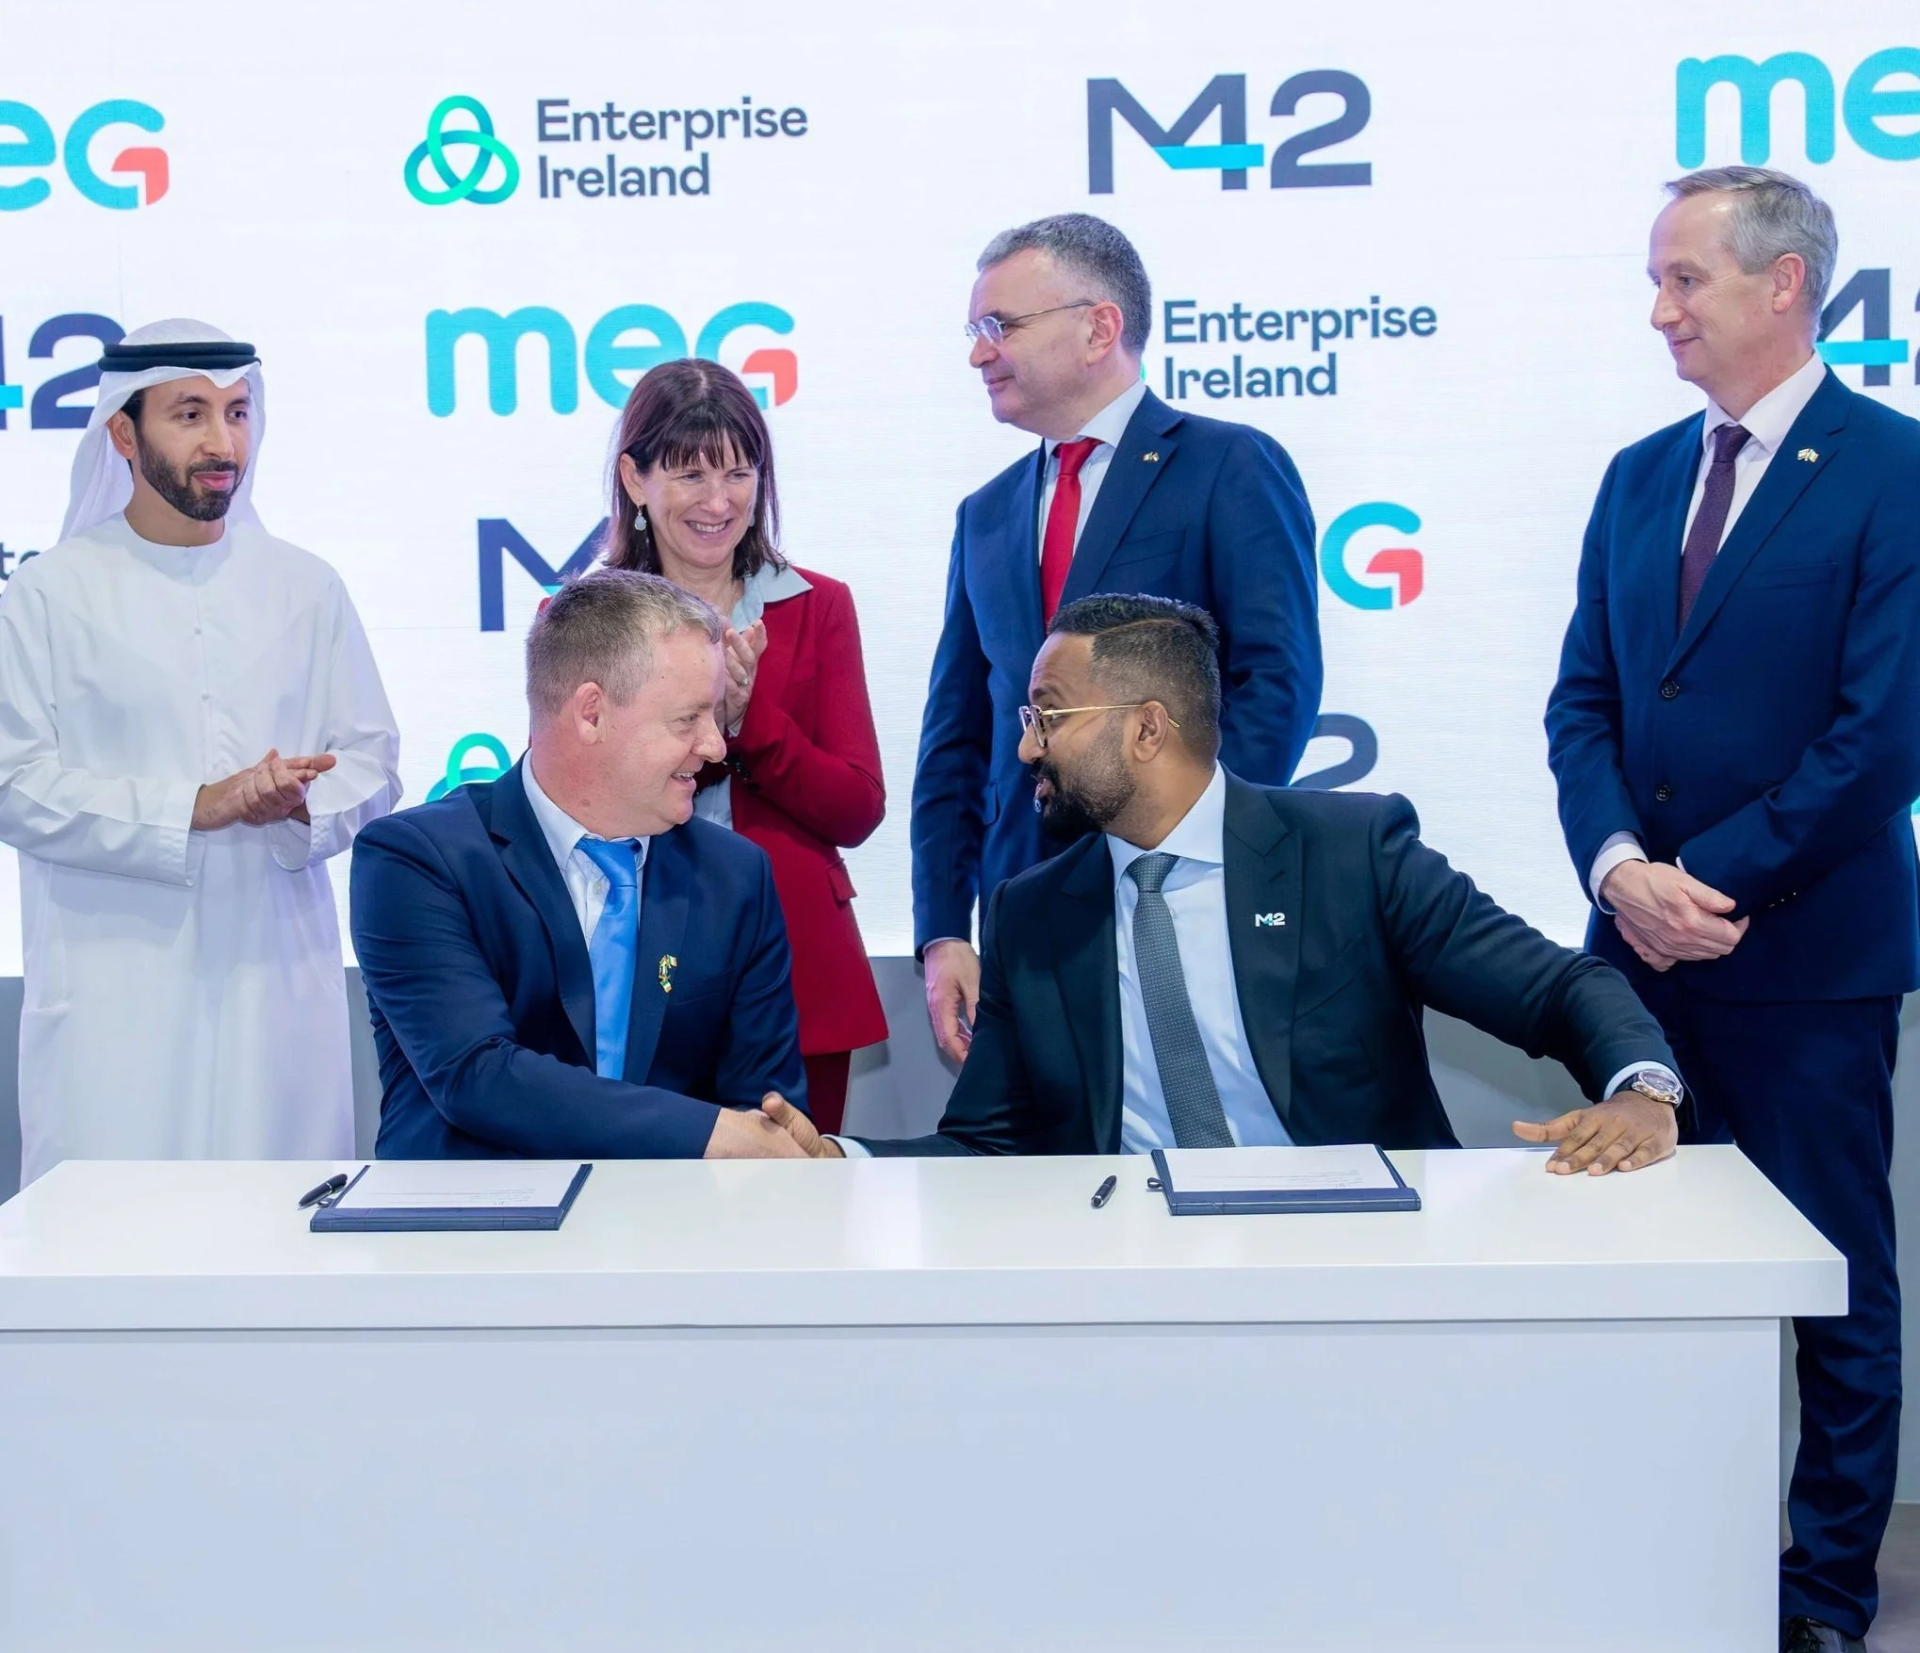
The same year also saw another significant milestone as MEG signed a major contract with M42, a global health-tech powerhouse with more than 20,000 employees and over 450 facilities across 26 countries.

2025 – Celebrating the Diversity Behind MEG

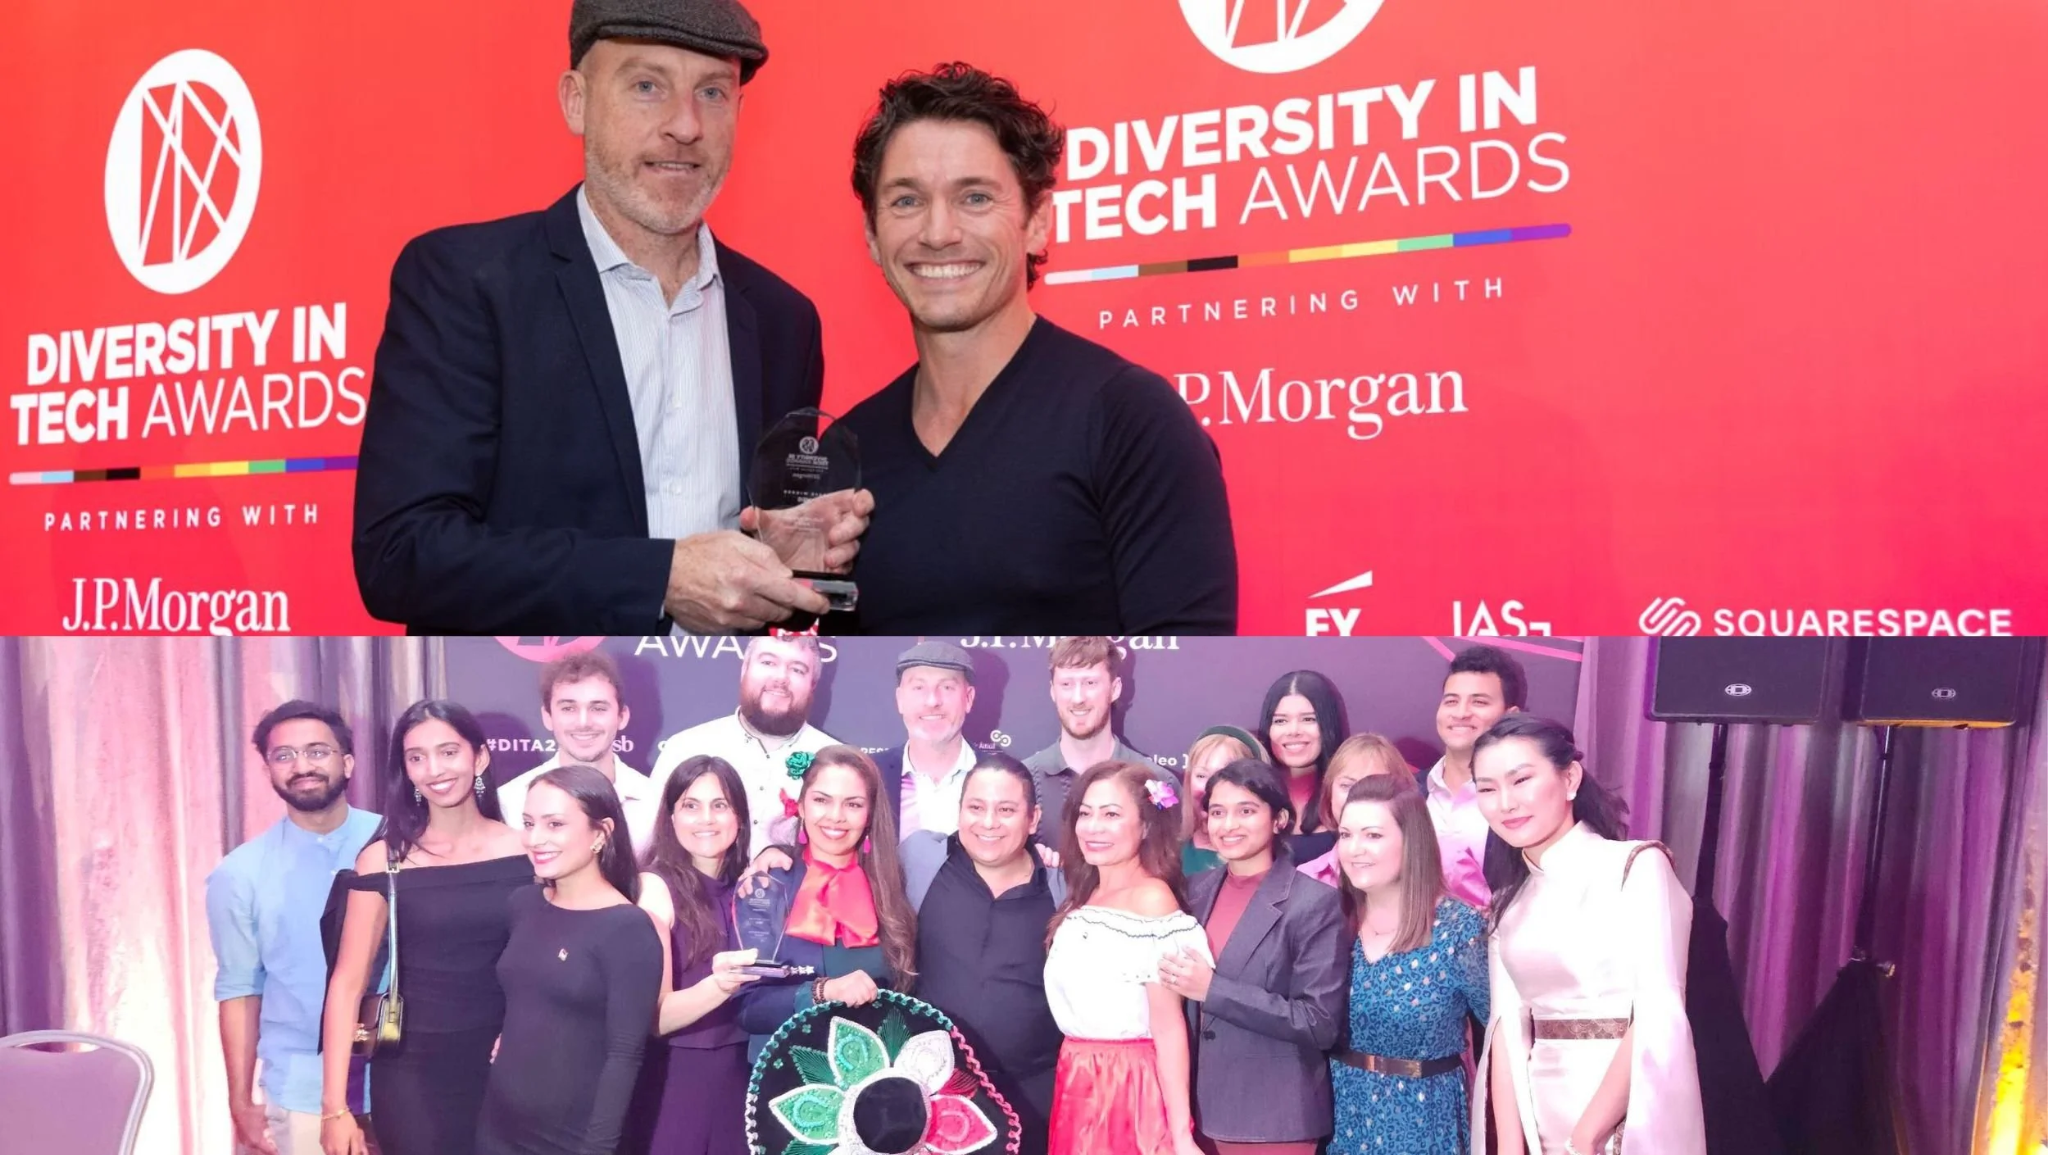
In 2025, MEG reached another proud milestone as the company won the Diversity in Tech Awards

By this stage, the team had grown to 65 people representing 31 nationalities and speaking more than 20 languages

What started as a small team in Dublin had evolved into a truly international company, bringing together different experiences, cultures and perspectives, all connected by the same shared mission of improving healthcare quality and patient safety. 

2026 – MEG Turned 10!

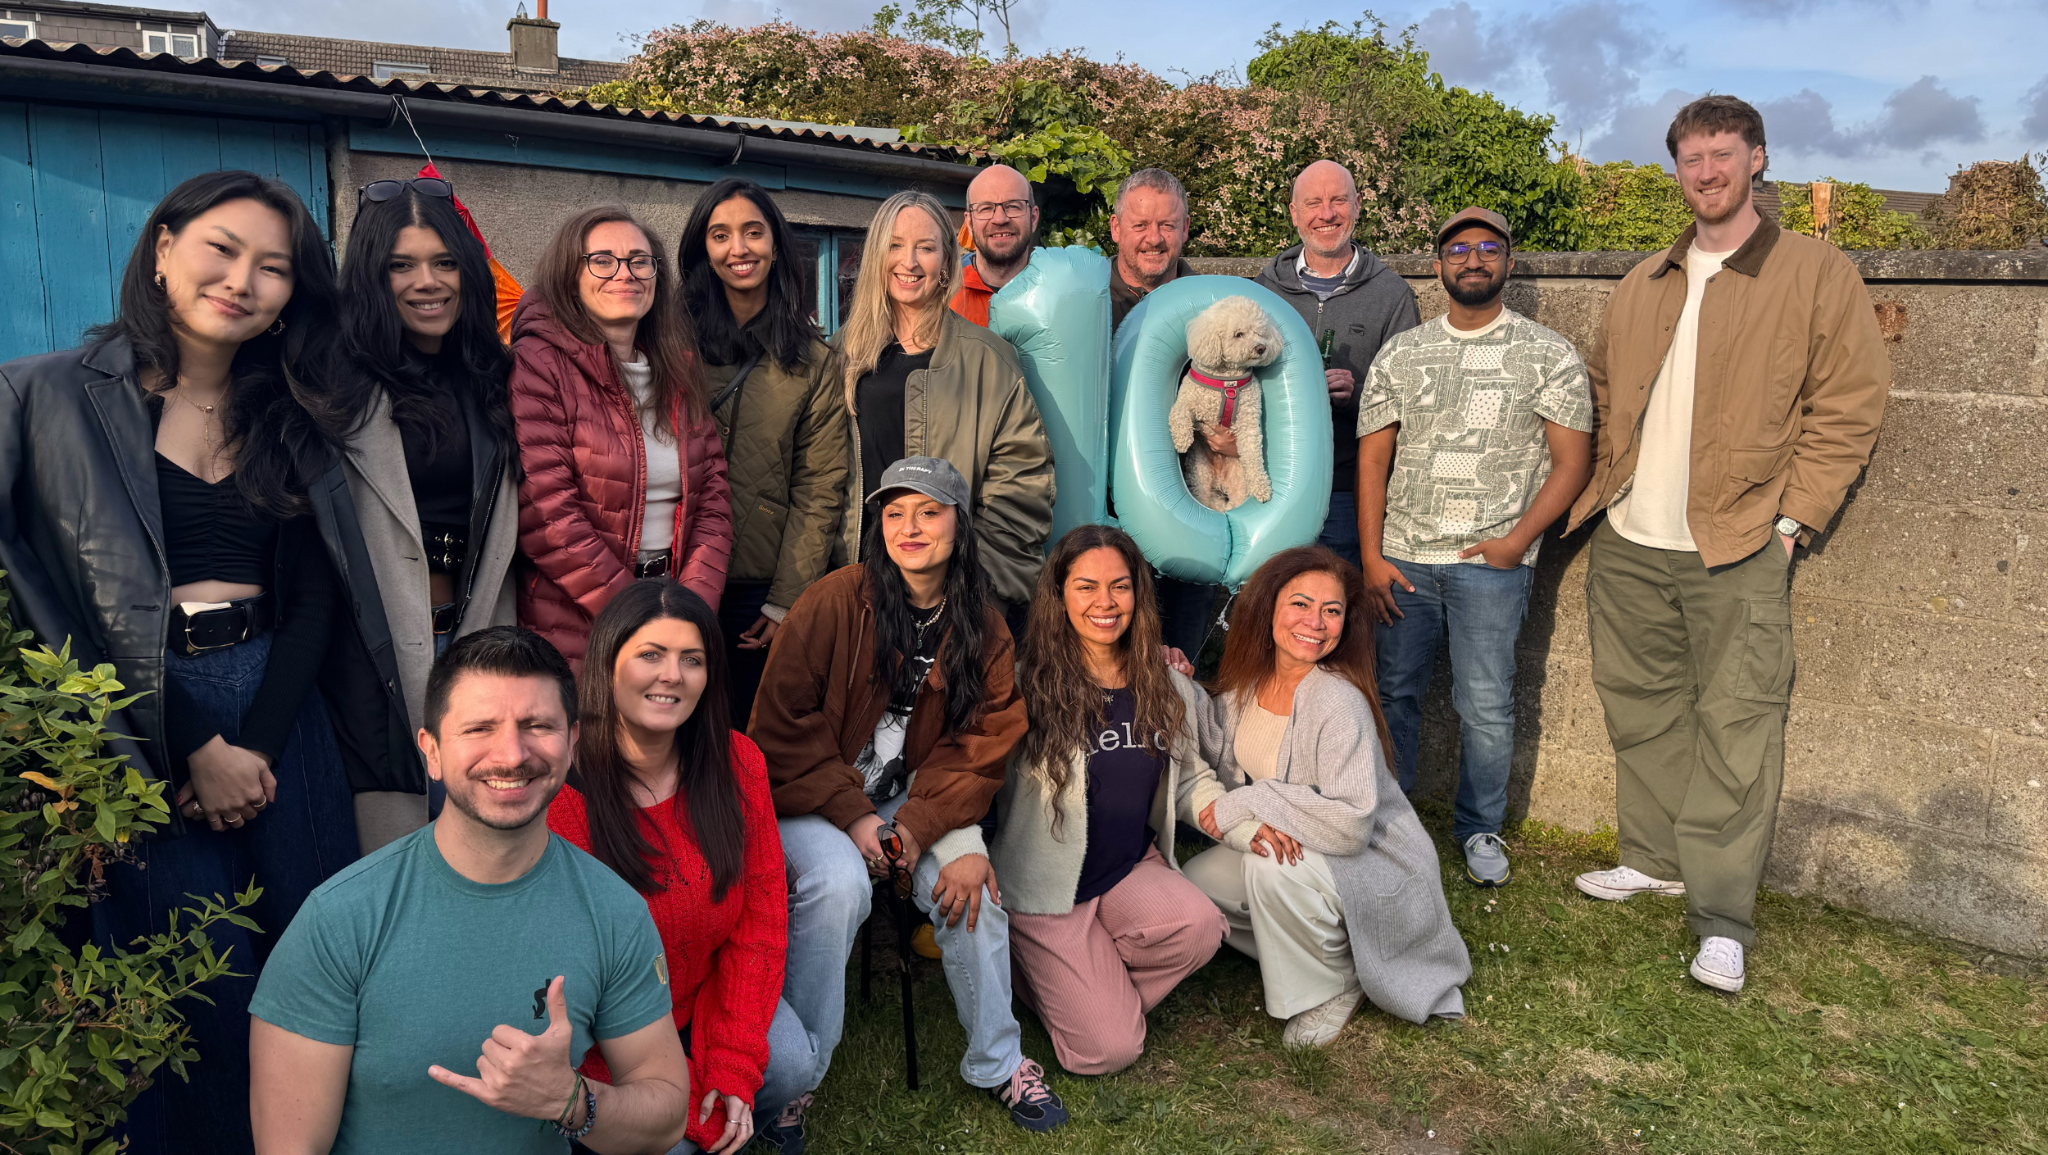
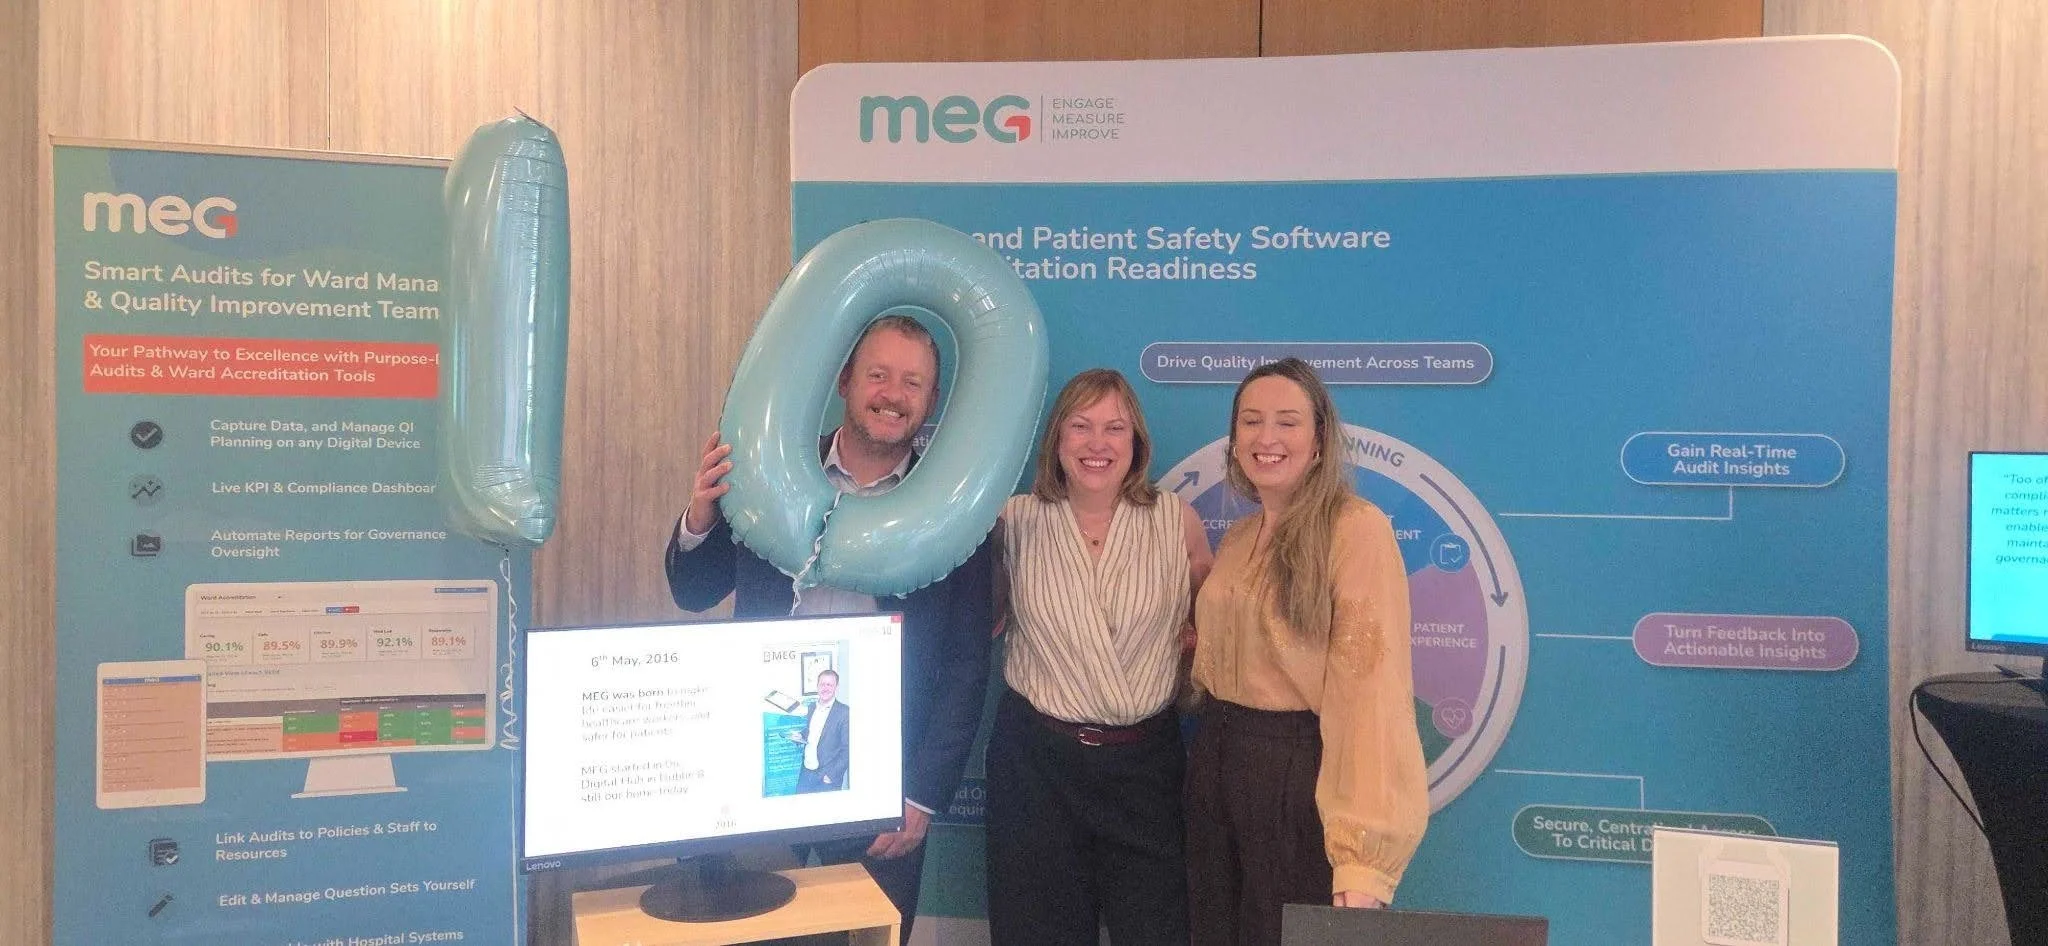
May, 2026 has been all about celebrating the people, partnerships and milestones that shaped the first 10 years of MEG. One of the proudest moments was sponsoring the IPC Ireland Annual Conference alongside IPCI as both organisations celebrated their 10-year milestones. At the pre-event dinner, Kerrill shared MEG’s journey with a room full of IPC professionals, many of whom had been part of that journey along the way.

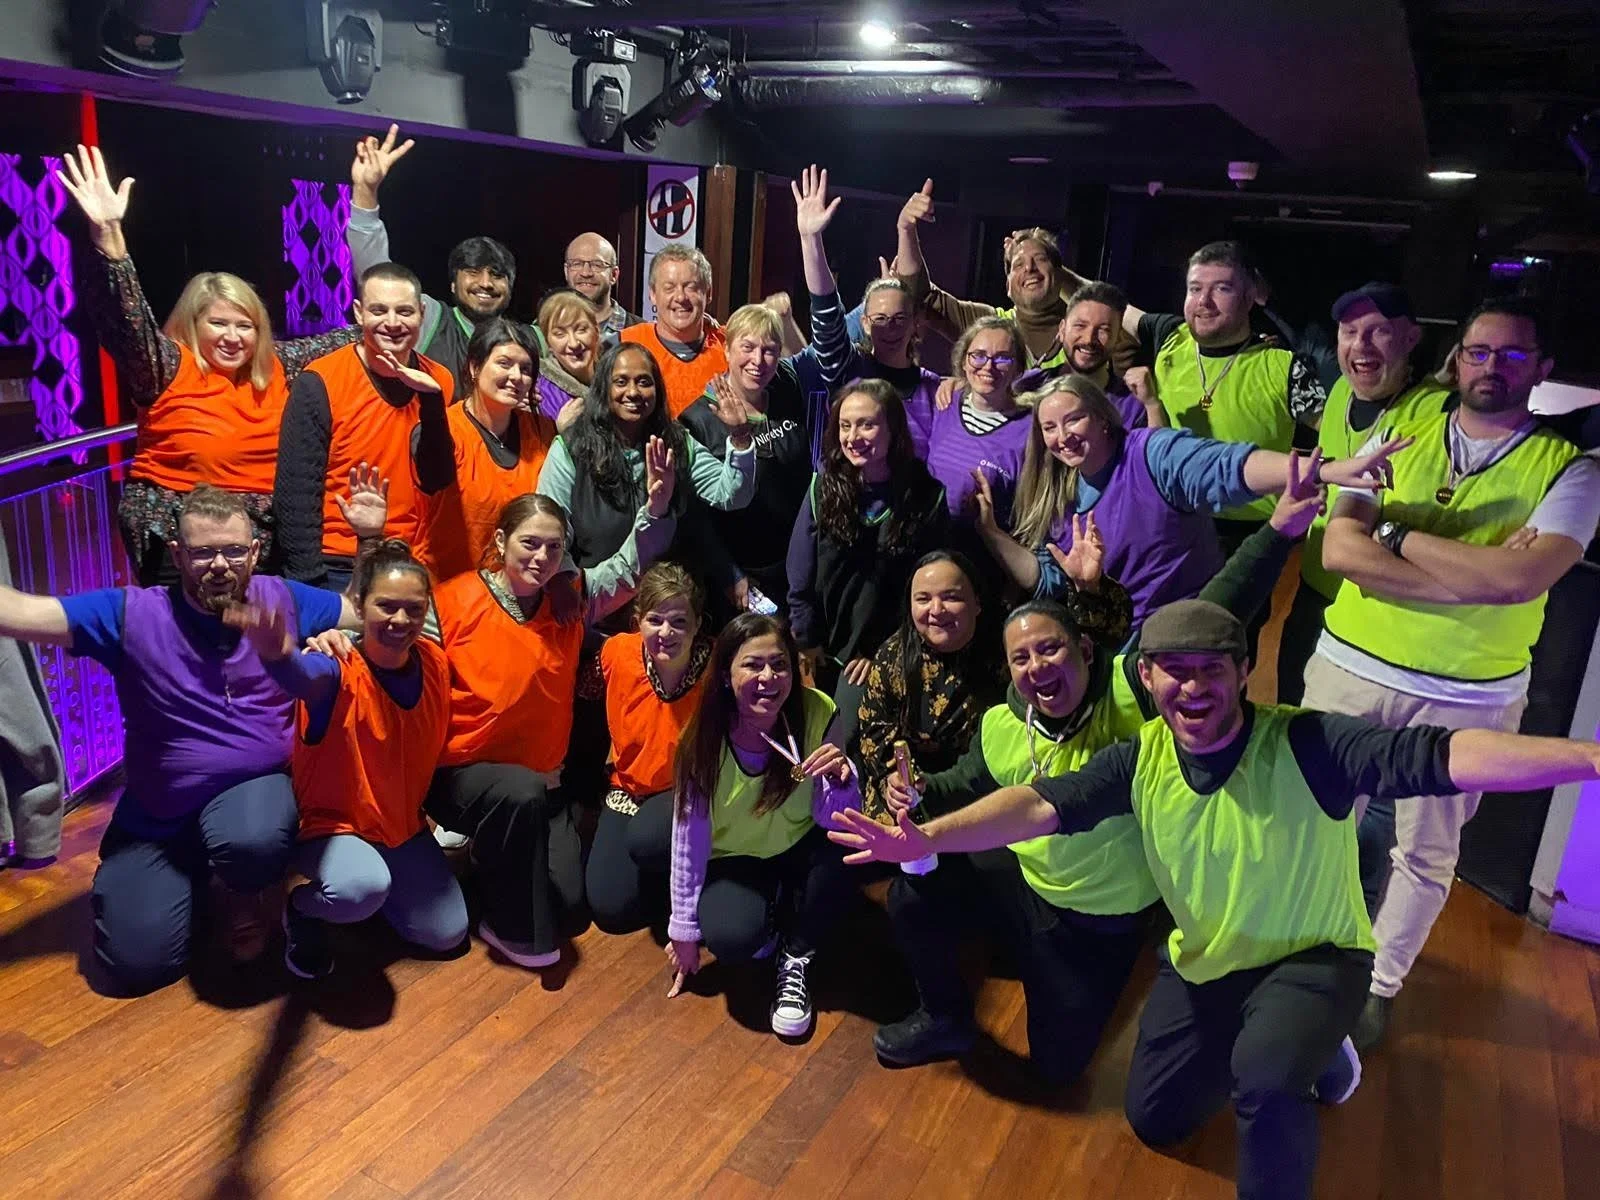
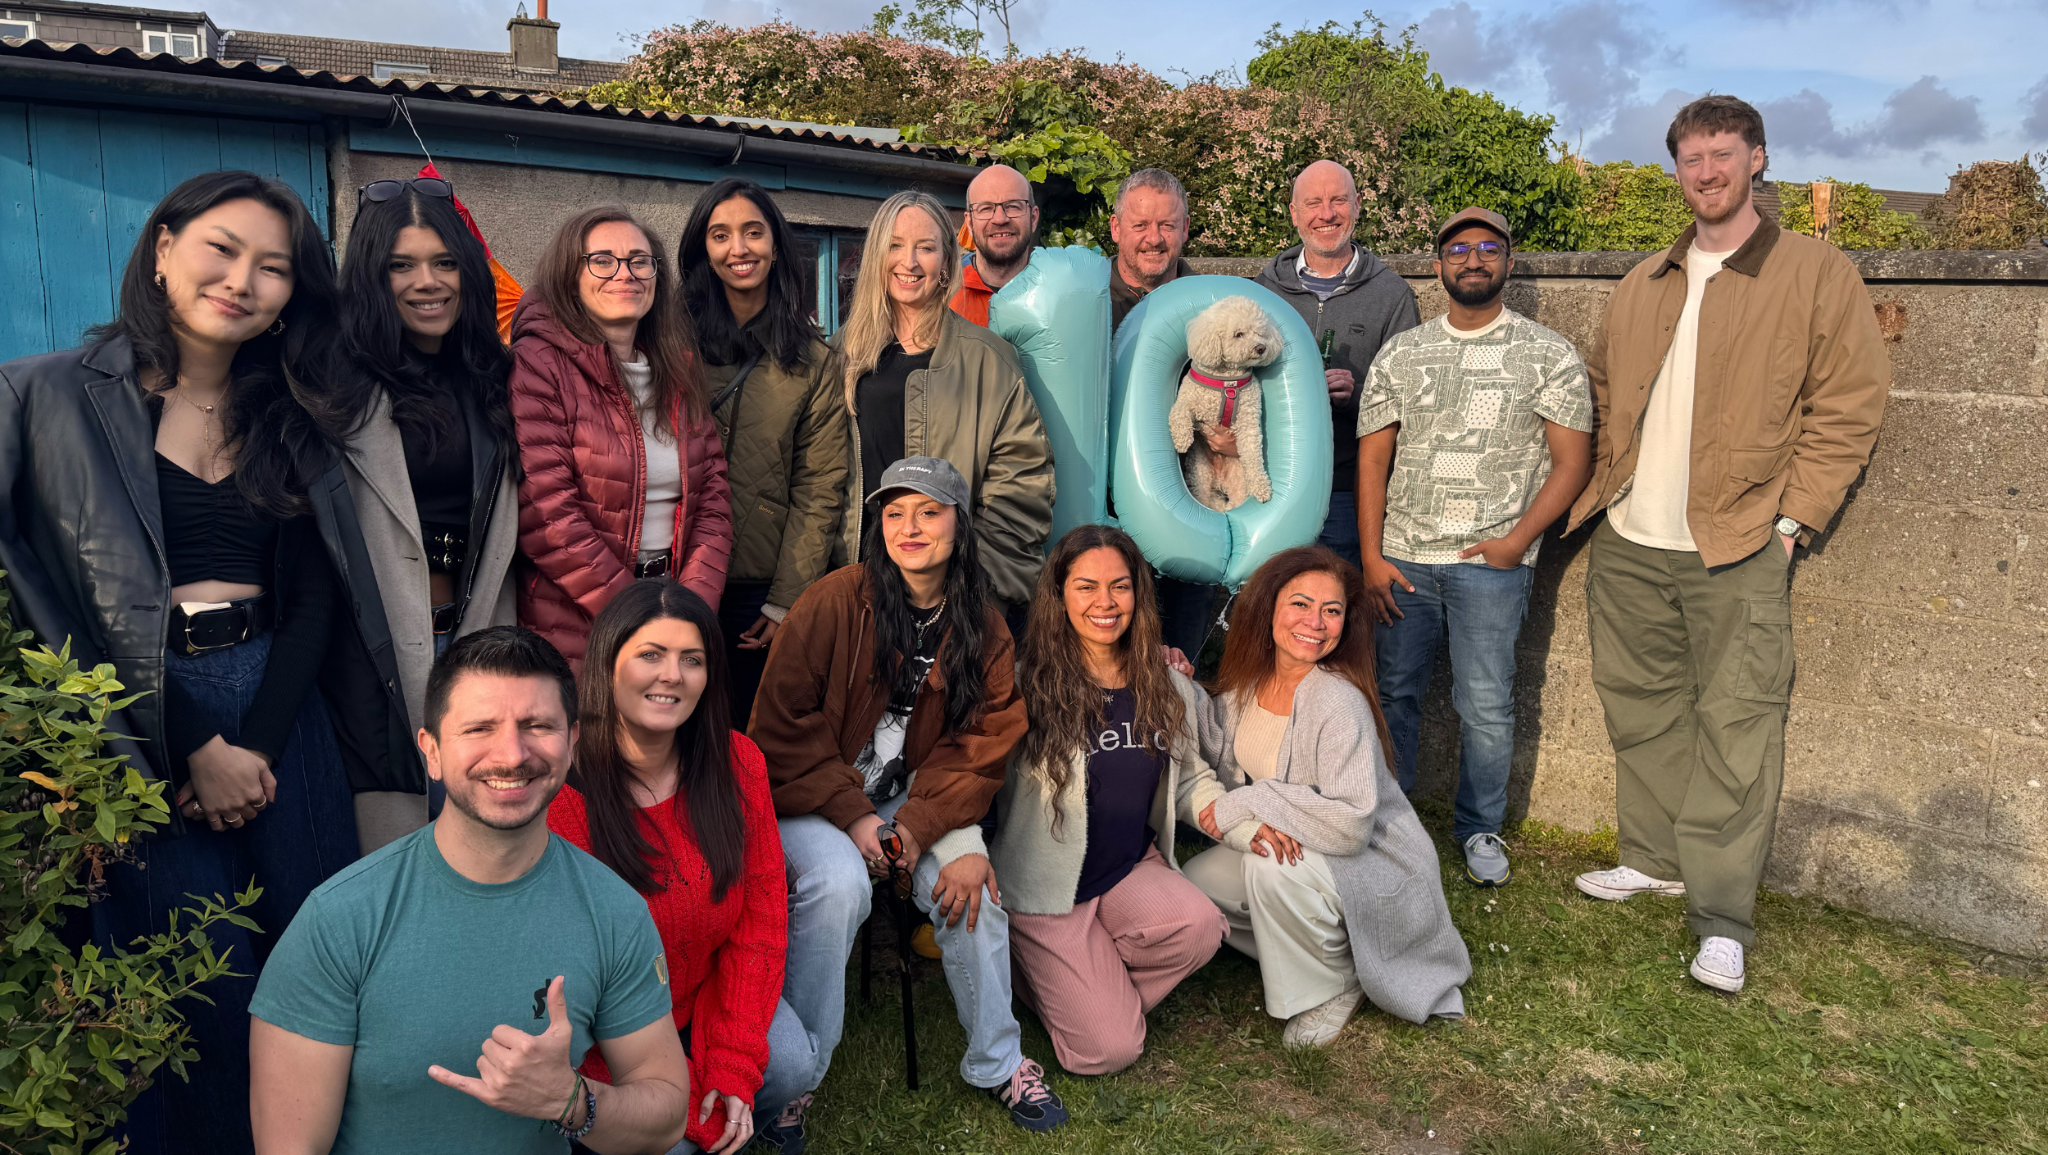
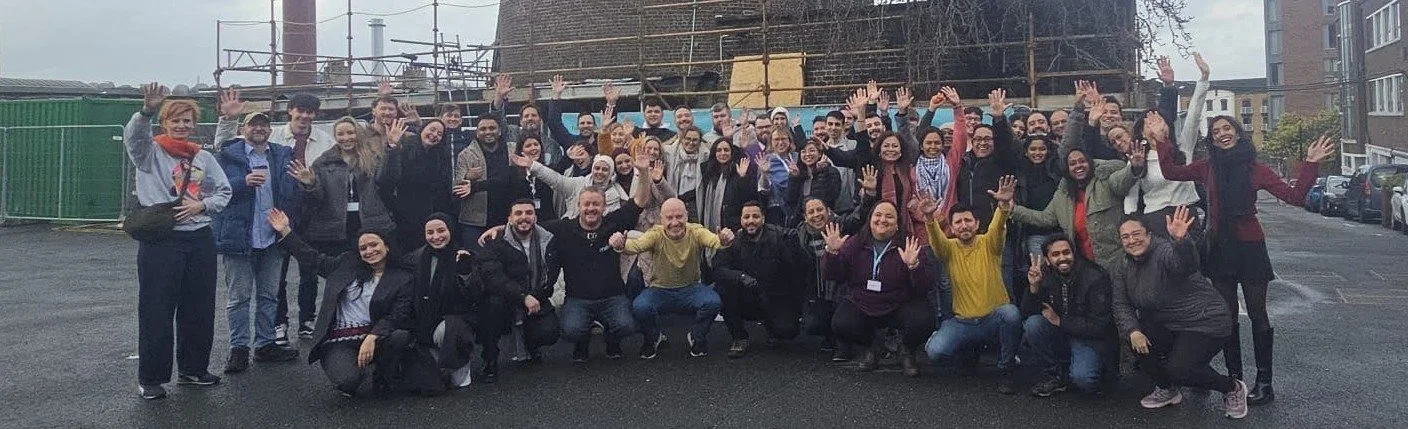
To round off the celebrations, some of the MEG crew gathered in Dublin for a celebratory BBQ.

Future with meg

As MEG celebrates its first decade, the future feels bigger than ever. Healthcare continues to evolve quickly, and quality, safety and governance teams are being asked to do more with greater speed, visibility and accountability.

Technology will play an important role in what comes next. Artificial Intelligence is already opening new possibilities, from helping teams identify trends sooner, to reducing administrative work, to making quality insights easier to act on.

But for MEG, innovation only matters if it supports the people at the centre of healthcare. The goal is not technology for its own sake. It is technology that helps frontline teams spend less time on manual processes and more time improving care.

If you want to go fast, you have to go alone and if you want to go far, you have to go as a team. I think this is where MEG’s future lives. We have to go far as a team.
— Anna Gularska, Technical Sales Support Manager

With more healthcare organisations, more countries and more innovation ahead, the team is incredibly excited for what comes next.

Thank You For Being Part of This Incredible Journey

Every step of MEG’s journey has been shaped by the people around us. To our customers, partners, team members and everyone who has supported MEG over the last 10 years, thank you for trusting us, challenging us, supporting us and growing alongside us.

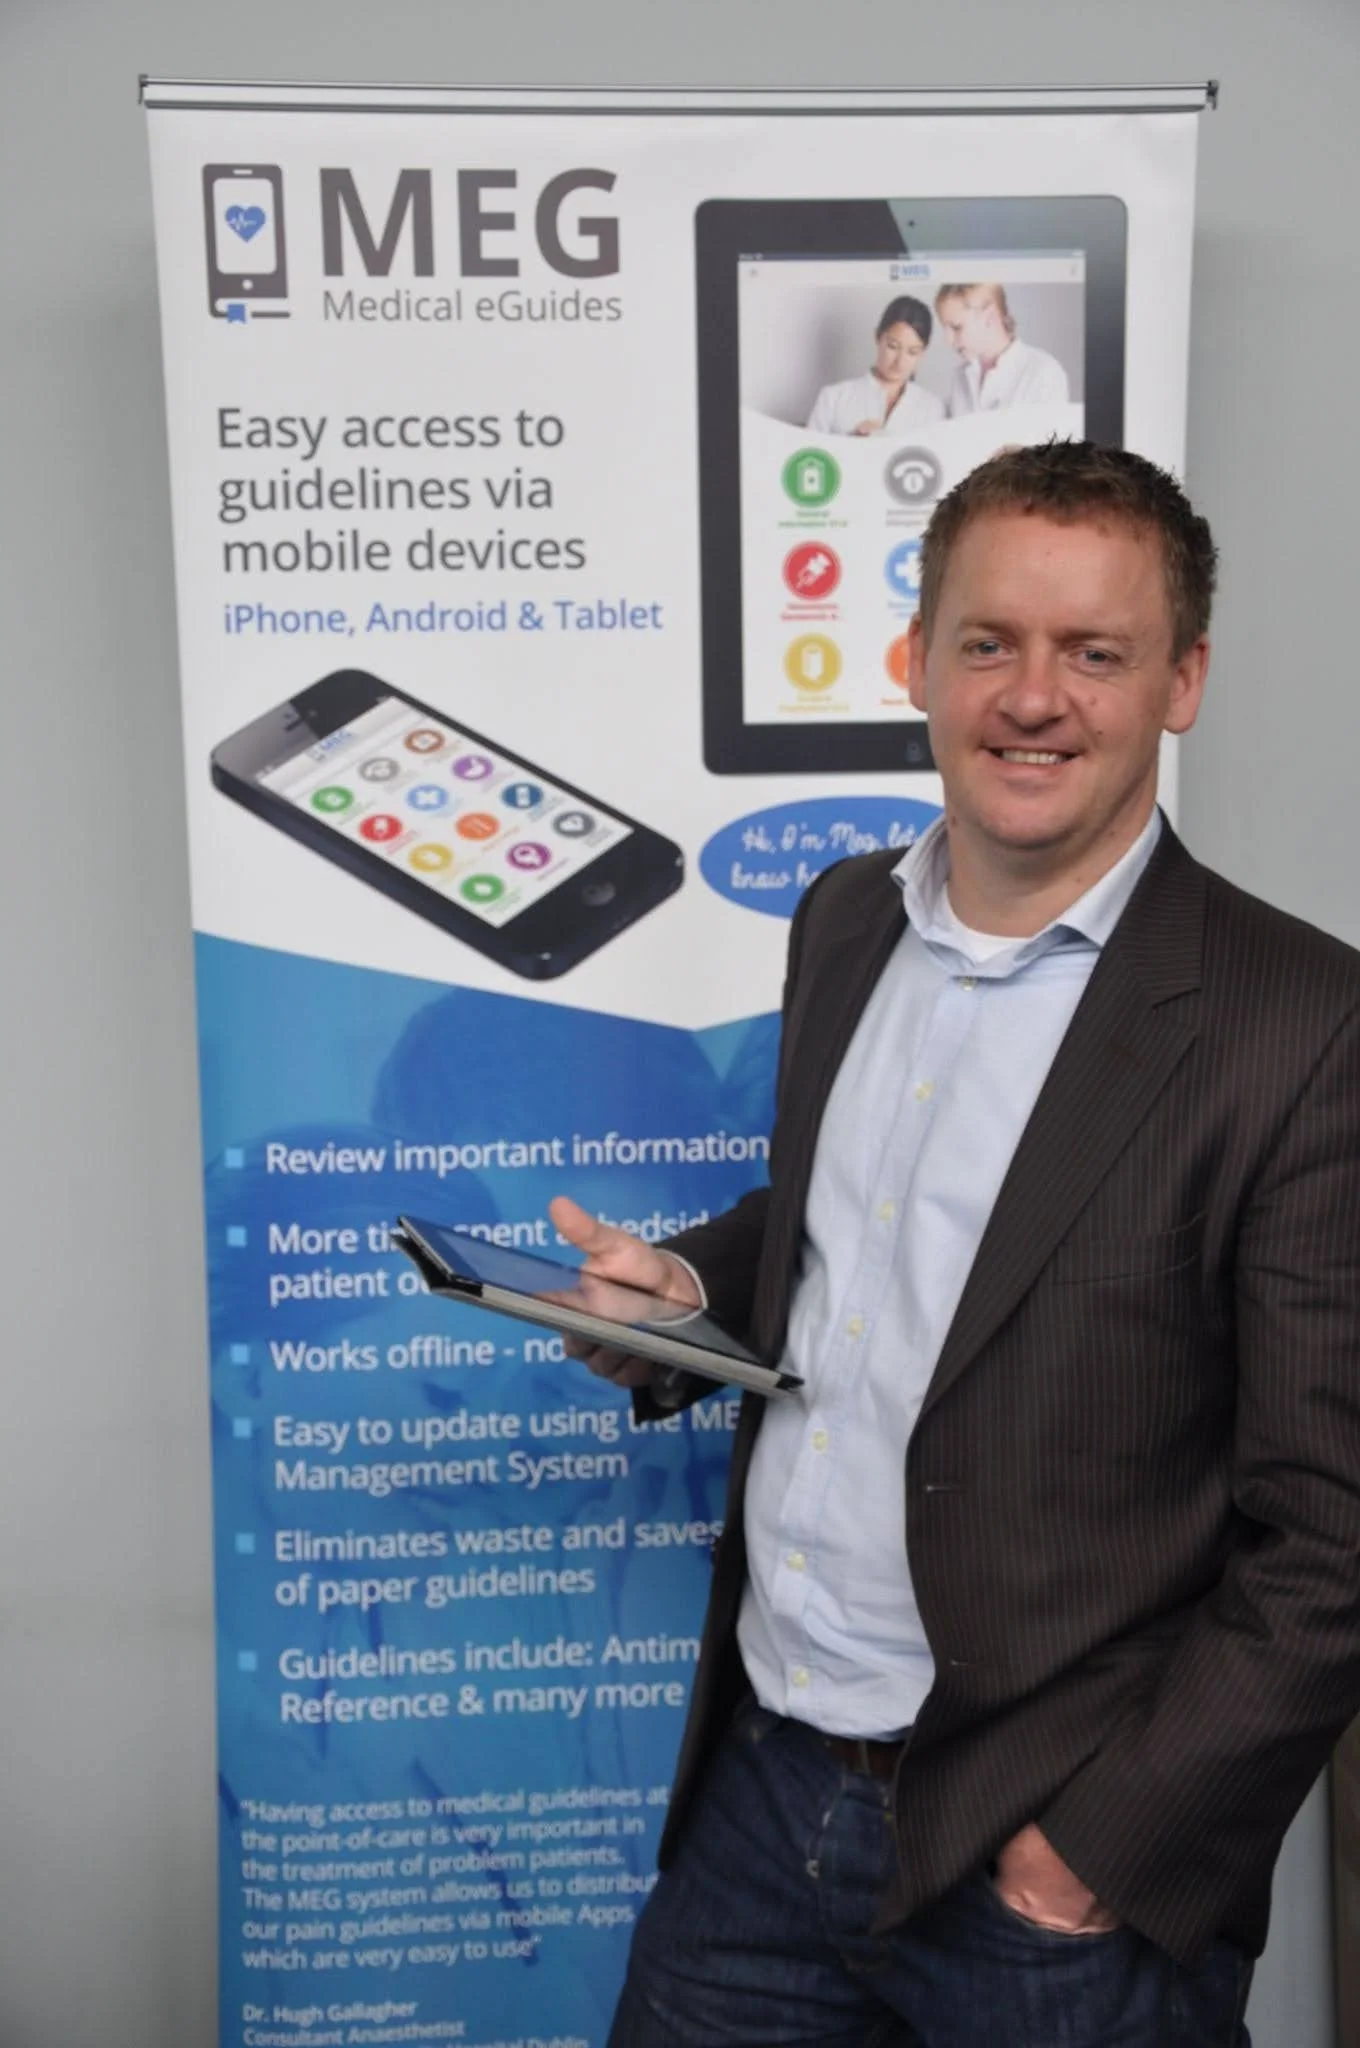
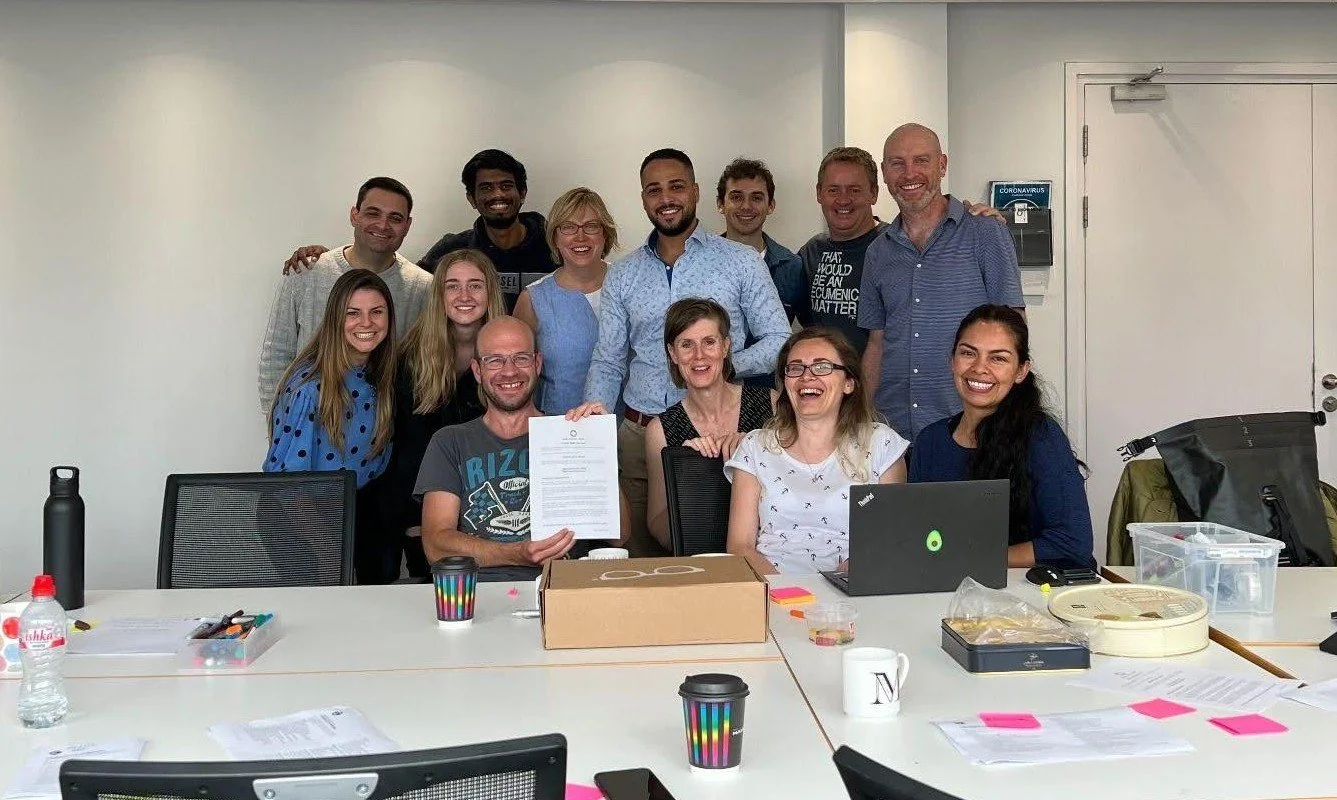
Our team in 2016

Our team in 2026

NHS Staff Survey 2025: The Gap Between Reporting Incidents and Taking Action

Each year, the NHS Staff Survey provides the most comprehensive insights into how care is delivered on the front line. With over 700,000 responses in 2025, the survey reflects the staff experience, the realities of patient safety and quality across the system.

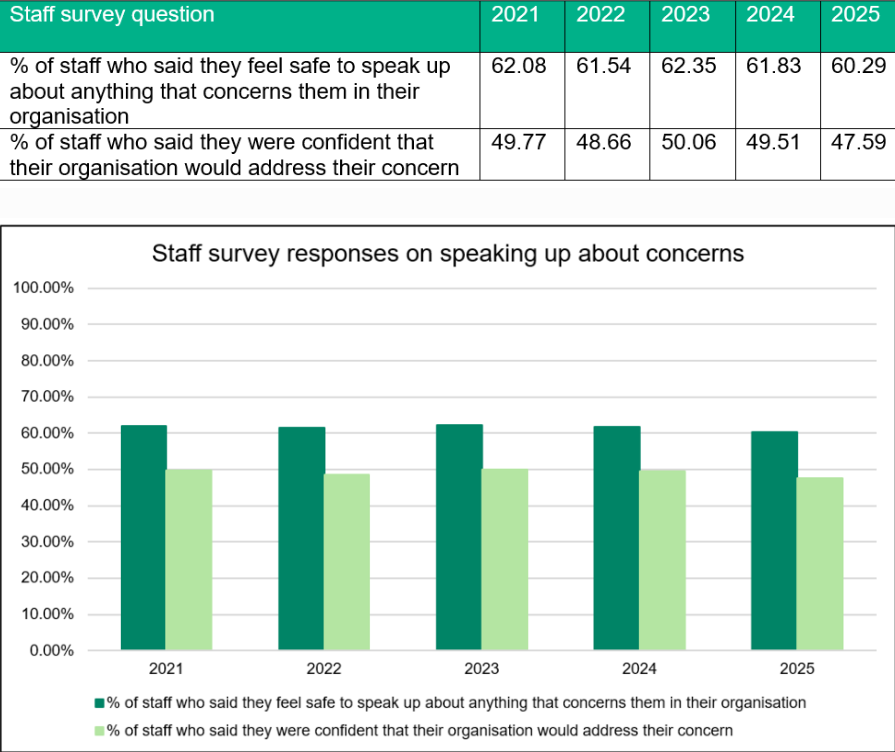
This year’s results show continued progress in building a culture where staff feel encouraged to report incidents and raise concerns, but the data also highlights a more persistent challenge – ensuring that what is reported is consistently followed through and leads to meaningful action, in an environment where teams are already stretched.

To understand where the gap lies, let’s look at three key areas highlighted in the survey and how they impact patient safety and improvement.

1. Strong reporting culture, but weak follow-through

According to the NHS Staff Survey 2025:

  • 33% of staff have seen incidents that could have harmed patients, yet only 67% say action is taken to prevent them from happening again, and just 61% receive feedback on changes made.

What this means

Patient safety risks are being identified, but not consistently translated into action or learning. Without clear follow-through and feedback, the same types of incidents are more likely to recur, and opportunities to strengthen safety systems are missed.

How MEG helps:

With MEG’s Incident Reporting & Risk Management Software:

  • Log incidents at the point of care via mobile or tablet, reducing delays and underreporting

  • Standardise reporting with configurable workflows and structured forms, ensuring consistent data capture

  • Each incident is automatically linked to action plans, risks, and investigations, ensuring it doesn’t sit in isolation

  • Assign, track, and escalate follow-up actions with clear ownership, deadlines, and real-time visibility 

  • Automated escalations and alerts ensure overdue actions are flagged and followed up

  • Real-time dashboards give visibility into incident trends, action status, and resolution rates

Impact

Clear ownership, visible follow-through, and stronger trust that reporting leads to real change.

2. Patient feedback is collected, but not consistently actioned

According to the NHS Staff Survey 2025

  • From 72% in 2021 to 69% in 2025 (-3%), there has been a steady decline in staff who believe organisations act on patient concerns

What this means

Patient insight is being captured, but not always used to drive improvement. When feedback is not linked to action, organisations miss valuable signals about emerging risks, patient experience gaps, and areas requiring immediate attention.

How MEG helps 

With MEG’s Friends and Family Test (FFT) tool, part of our  Patient Experience software:

  • Capture patient feedback across multiple channels, including SMS, QR codes, kiosks, email and web, improving response rates

  • Use AI-powered analysis to automatically identify themes, sentiment, and emerging patient safety risks from free-text feedback, delivering actionable insight in real time

  • Automatically route feedback to the right teams with instant notifications, ensuring clear ownership, faster response, and timely resolution of concerns

  • Connect feedback directly to action plans, incidents, and risk registers within a single system, enabling trackable, measurable improvement

Impact

Patient voice becomes actionable insight, not just collected data, driving continuous service improvement.

3. Patient care is the priority, but resources are stretched

According to the NHS Staff Survey 2025

  • 72% say patient care is the top priority, but only 56% feel they have adequate materials, supplies, and equipment to deliver that care

  • Only 33% say there are enough staff, and only 47% of staff said that they can meet demands on time at work

What this means

Teams are committed to delivering safe, high-quality care, but limited time and resources make it difficult to act on incidents, feedback, and improvement plans. As a result, actions are delayed, follow-through becomes inconsistent, and improvement efforts struggle to keep pace with day-to-day demands.

How MEG helps

With MEG’s End-to-End Quality Management Platform - your digital extension of the team:

  • Capture data at the point of care with a mobile-first platform across incidents, audits, risks, and feedback

  • Automate workflows to reduce manual admin and remove reliance on spreadsheets and emails

  • Connect incidents, risks, audits, and feedback in one system, feeding directly into action planning

  • Provide real-time visibility through centralised dashboards for both frontline teams and leadership

  • Enable structured action planning and tracking, ensuring tasks are assigned, monitored, and completed without added burden

Impact

Less admin, faster follow-through, and more capacity for teams to focus on delivering safe, high-quality care.


When these gaps persist, the impact is felt across staff experience and patient safety.
❌ Incidents are more likely to be repeated, as underlying risks are not fully addressed
❌ Learning is delayed, with insights not consistently translated into action
❌ Confidence in reporting systems begins to erode

High-performing healthcare teams take a different approach. They move beyond capturing data and focus on connecting it, bringing incidents, risks, audits, and feedback into one system that feeds directly into clear, trackable action plans with defined ownership and real-time visibility. This means issues are not just recorded, but resolved, trends are identified earlier, and teams can act before risks escalate.

👉 If you’re looking to strengthen follow-through and make every insight count, book a 15-minute discovery call to see how MEG can support your team.