[Part 1] The Digital Document Graveyard: Why Legacy Systems Still Put Healthcare at Risk

The dusty binders may be gone. Walk into most hospitals today, and you’ll find fewer filing cabinets stuffed with outdated policies. Instead, the graveyard has moved online.

Today’s “document graveyard” is SharePoint sites, intranet folders, and static PDF repositories. Policies technically exist in digital form, but for frontline staff, they might as well be buried six feet under. Clunky navigation, siloed folders, and poor search functionality mean that critical documents are effectively invisible when they’re needed most.

The risks are no less real than in the paper era. They may be greater. When leaders believe they’ve modernised simply because documents are “online,” they risk overlooking the ways these legacy digital systems fail to protect staff, patients, and the organisation itself.

Clinical Risk: When ‘Online’ Isn’t Accessible

In healthcare settings, SharePoint and intranet-based repositories were an important first step in moving away from paper-based policy management. But they were never designed for the complex demands of modern healthcare. These systems are effective at storing documents, yet storage alone isn’t enough when staff and regulators need instant access, clear version control, and evidence of staff attestation.

The result?

Staff waste valuable time scrolling through endless lists of documents.
❌ Different teams create duplicate versions, leading to confusion about which is correct.
❌ Staff rely on memory, peer advice, or outdated hard copies because they can’t reliably find what they need.

Clinical risk doesn’t just come from the absence of policies. It also comes from policies that staff can’t quickly find, trust, or use.

“Healthcare can’t afford to treat policy management as an administrative afterthought. Outdated or inaccessible documents don’t just create inefficiency, they put patients, staff, and organisations at real risk.”
— — Clare Harney, Healthcare Policy Expert

Compliance Risk: Regulators Aren’t Fooled

Healthcare regulators expect more than “documents stored somewhere online.” All require clear version control, audit trails, and demonstrable accessibility as a minimum standard.

Legacy systems often fall short:

  • Multiple versions of the same policy may live in different folders.

  • No reliable audit trail shows who reviewed or approved changes.

  • Surveyors asking “show me the policy” are met with frantic searches and uncertain results.

Most critically: attestation is nearly impossible.

  • SharePoint and intranets can’t track whether staff have actually opened, read, and acknowledged a policy.

  • There’s no way to assign policies to specific roles and capture individual attestations.

  • Leaders are left hoping staff are compliant — but with no evidence to prove it when regulators ask.

In compliance terms, “we emailed it” or “it’s in SharePoint” doesn’t demonstrate accountability. Regulators want to see that staff received, read, and signed off on policies — and that organizations can prove it with a clear audit trail.

Cultural Risk: The Cost of Mistrust

Culture is built on trust. Staff need to believe that leadership equips them with the tools and information to succeed.

When staff can’t reliably find policies, frustration grows. Over time, disengagement sets in. They create workarounds, pass around shadow documents, or simply rely on “what we’ve always done.”

This doesn’t just weaken compliance; it corrodes culture. Staff begin to assume leadership doesn’t prioritise their needs. That mistrust spreads, undermining safety culture and reducing adherence to policies across the board.

A graveyard system doesn’t just bury documents. It buries staff morale.

The Illusion of Modernisation
The danger of legacy digital systems is that they create a false sense of progress. Leaders may think, “We’ve digitised our policies, so we’re fine.”

But digitisation is not the same as accessibility. Putting binders online doesn’t solve the problem; it only relocates it.

If a nurse spends 10 minutes searching for the infection control policy…
If a compliance officer can’t instantly demonstrate the current version to an inspector or accreditation surveyor…
If a new junior doctor downloads an outdated PDF from a shared drive…

…then the system isn’t modern. It’s a digital graveyard, and the risks are very much alive.

Why This Matters Now

Healthcare is under more pressure than ever:

  • Staffing shortages mean new hires must be onboarded quickly and reliably.

  • Regulatory scrutiny is increasing, with zero tolerance for “we couldn’t find it.”

  • Patient safety demands require information that is trusted, consistent, and easy to locate in the moment of need.

Legacy digital systems were an important step away from paper, but they simply weren’t built for this environment. What’s needed is not just digitisation, but transformation: systems designed for findability, trust, and accountability.

Retiring the Digital Graveyard

It’s time to face reality: SharePoint and other intranet repositories were built for document storage, not for the complex demands of healthcare policy management. They remain useful as general collaboration tools, but they can’t provide the speed, visibility, and proof that today’s healthcare environment requires.

Healthcare leaders must demand more:

  • Powerful search that delivers the right policy in seconds.

  • Real-time version control that eliminates duplicates and confusion.

  • Audit trails and reporting that satisfy regulators.

  • Attestation tools that prove staff have read and understood critical policies.

The graveyard metaphor still applies but the solution is clear. Policies must be living documents, searchable in seconds, validated by audit trails, and supported by staff attestations.

Conclusion

The binders may be gone, but the graveyard remains. It lives in outdated digital systems that are siloed, clunky, and difficult to search with confidence.

Legacy systems multiply clinical, compliance, and cultural risks. And in a healthcare environment where every second counts, that’s unacceptable.

Healthcare leaders must move beyond the illusion of digitisation. Retiring the digital graveyard means adopting policy management systems that are dynamic, searchable, and accountable.

Because when policies are buried, whether in basements, in outdated PDFs, or in SharePoint with no proof they’ve been read, risk comes to life.

👉 In Part 2, we’ll explore how MEG transforms document management from a passive repository into a living, connected quality engine, giving healthcare leaders the tools to reduce risk, improve compliance, and empower staff with information they can trust.


Watch the On-Demand Webinar

Want to explore practical steps for moving beyond the “digital graveyard”? Watch our on-demand webinar:

Is Your Document System Driving Improvement, Or Just Storing Policies?
🎙 Featuring Clare Harney, Head of Advisory & Education Services at Santegic, and Leonora O’Brien, Chief Growth Officer at MEG

King's College Hospital London – Jeddah chooses MEG as digital partner for clinical governance

MEG is delighted to announce our partnership with King's College Hospital London – Jeddah, the Kingdom's first UK-branded hospital and a flagship healthcare collaboration between the UK and Saudi Arabia. King's College Hospital London – Jeddah joins our growing family of prestigious healthcare clients committed to governance excellence, alongside facilities such as Tallaght University Hospital (Ireland), M42 (Abu Dhabi), and Reem Hospital (Abu Dhabi).

King's College Hospital London – Jeddah

King's College Hospital London – Jeddah opened its doors in February 2025 as a purpose-built, state-of-the-art medical facility on Jeddah's prestigious waterfront. Fully integrated with its London counterpart, the hospital represents a major milestone in Saudi Arabia's healthcare transformation under Vision 2030.

The hospital provides comprehensive healthcare services with planned Centres of Excellence in Women's Health, Cardiology, Metabolic Disease, and Orthopaedics, delivering world-class medical care that meets both UK clinical standards and Saudi regulatory requirements.

Why Choose MEG?

As Saudi Arabia's first UK-branded hospital, King's College Hospital London – Jeddah required a governance platform that could seamlessly integrate international best practices with local compliance standards, from day one of operations.

The hospital's leadership team recognised that traditional paper-based risk management and patient safety processes would not align with their vision for digital excellence and operational efficiency. They needed a comprehensive solution that would support both local and international healthcare standards while delivering the unified, scalable governance framework essential for world-class care delivery.

In just a few months, MEG's integrated platform was implemented to power the hospital's complete governance ecosystem, including:

  • Incident and Medication Error Reporting – real-time tracking, root cause analysis, and learning loops to prevent recurrence

  • Risk Register & M&M Reviews – tools for proactive risk identification and structured case reviews that support evidence-based decisions

  • Audit & Committee Management – end-to-end workflows to meet accreditation standards and maintain regulatory readiness

  • Task Tracking & Action Plans – clear accountability, follow-ups, and transparency across departments

  • Centralised Document Control – one platform to manage clinical guidelines, policies, safety manuals, and more with audit trails and version control built in

Together, these modules helped build a digital-first governance model aligned with both international best practices and Saudi Arabia's accreditation expectations.

A key focus area has been the development of comprehensive medication error and adverse drug reaction reporting capabilities, which have significantly strengthened patient safety practices across the hospital.

The new reporting system has been transformative. It helped identify trends, reduce adverse events, and promote a culture of transparency and accountability among clinical teams. MEG’s collaboration and flexibility were key to building a module that supports continuous improvement.
— Ali Saber, Head of Pharmacy at King's College Hospital London – Jeddah

"We're proud to support King's College Hospital London – Jeddah in its mission to deliver world-class care," said Nabeel Deek, MEG's Regional Business Development Manager – MENA. "This collaboration reflects our commitment to advancing healthcare innovation across the region and supporting Saudi Arabia's Vision 2030 goals."

As the hospital expands its Centres of Excellence across multiple specialties, MEG will continue to provide the digital infrastructure to support transparent governance, safe care, and continuous improvement.

The MEG team looks forward to supporting King's College Hospital London – Jeddah as it establishes new benchmarks for healthcare excellence in the Kingdom, demonstrating how governance systems can be proactive, integrated, and foundational to high-quality care delivery.


For more information about MEG and our healthcare governance solutions, visit www.megit.com

MEG Achieves SOC 2 Type II Attestation!

At MEG, protecting sensitive healthcare data is a core part of who we are. That’s why we’re thrilled to announce that MEG has achieved the prestigious SOC 2 Type II attestation, a globally respected benchmark that reflects our commitment to privacy, security, and operational integrity.

We recently spoke with Guvanch Meredov, MEG’s Head of Compliance and Data Protection Officer, to learn more about what this milestone means for MEG, our customers, and the wider healthtech ecosystem.

In this blog, you'll discover:

  • What is SOC 2 Type II and why does it matter?

  • What does SOC 2 Type II evaluate?

  • How MEG Achieved SOC 2 Type II

  • What does this mean for our customers and partners?

  • What’s next in MEG’s compliance journey

  • Final Reflection

What is SOC 2 Type II and why does it matter?

SOC 2 Type II is one of the highest security standards in SaaS. Developed by the American Institute of Certified Public Accountants (AICPA), it goes beyond a one-time review, instead, it evaluates how effectively an organisation operates its data protection and security controls over 12 months.

While SOC 2 Type I assesses design at a single point in time, Type II proves that those controls are consistently implemented over months of real-world operation.

SOC 2 Type II  shows that our controls don’t just exist on paper, they’re consistently applied in real operations.
— Guvanch Meredov, Head of Compliance/DPO at MEG

For healthcare providers and regulated organisations working with us, this is a meaningful assurance - MEG can securely manage their sensitive data at scale with the highest standards of protection.

What does SOC 2 Type II evaluate?

The audit evaluates MEG’s controls across five key trust service principles:

  • Security — Protecting data against unauthorised access

  • Availability — Ensuring systems are reliable and operational

  • Confidentiality — Keeping sensitive information private

  • Processing Integrity — Ensuring systems operate correctly and without error

  • Privacy — Safeguarding personal data in line with regulations

The scope included our cloud infrastructure, encryption protocols, access controls, incident response, and more, providing a thorough evaluation of both technical and procedural safeguards.

How MEG Achieved SOC 2 Type II

Our attestation covers June 2024 through May 2025, and was the result of a sustained, company-wide effort. The journey included:

  • Scoping and defining systems under audit

  • Implementing and refining controls aligned with trust service criteria

  • Rigorous internal readiness checks

  • Extensive evidence gathering to demonstrate compliance in practice

  • Third-party validation and testing

This builds on MEG’s existing ISO 27001 certification and GDPR adherence, enabling us to maintain a high standard of trust and transparency.

What does this mean for our customers and partners?

Whether you're an existing customer or evaluating MEG, this attestation brings key advantages like:

  • Independent validation of our ability to manage sensitive data securely

  • Alignment with major compliance frameworks — including GDPR, ISO 27001, Cyber Essentials, and the NHS DSPT

  • Faster procurement and onboarding, thanks to verifiable third-party assurance

  • Increased credibility with public sector buyers, supported by our UK G-Cloud 14 listing

Clients can also request executive summaries, audit reports, or attestations to support their own compliance requirements.

For our customers, it provides independent assurance that MEG can safely manage, process sensitive healthcare data at scale

What’s next in MEG’s compliance journey

SOC 2 Type II attestation is a major milestone but not the finish line. MEG is committed to ongoing compliance through:

  • Annual ISO 27001 and SOC 2 Type II surveillance audits

  • Biannual penetration tests and vulnerability scans

  • Continuous staff training and policy reviews

  • Automated real-time monitoring of security controls

  • Regular GDPR Data Protection Impact Assessments (DPIAs) and related processes

With growing interest in US and international markets,MEG is aligned with HIPAA requirements and is scheduled for an external audit to validate compliance in Q4 2025.

Final Reflection

SOC 2 Type II is more than a logo or a line on a slide. It reflects the reality that when organisations trust MEG, they’re trusting us with something sacred—the safety, privacy, and dignity of people’s health data.
We take that responsibility seriously. And now, we have the audit to prove it.

Want to review our SOC 2 report? Reach out at dataprotection@megit.com


If you are interested in discovering how MEG can meet your data protection, operational, and regulatory needs, our team is here to help.

Making Dashboards Part of Governance Culture

Example of a live MEG dashboard showing CQC domains with RAG ratings

Introduction: Dashboards Are Only Useful If They're Used

Dashboards are everywhere in healthcare. But in governance?
They’re only as valuable as the conversations they support.

We’ve seen NHS teams build beautiful, detailed dashboards, only to realise they’re not actively shaping board reporting, clinical decision-making, or team priorities. That’s not a tech problem. It’s a cultural one.

In this post, we explore what happens when dashboards move from back-room reporting to frontline governance tools. It’s based on what we’ve learned from NHS Trusts using MEG to embed dashboards into meetings, workflows, and assurance frameworks - not just to see performance, but to act on it.

Table of Contents

  1. The Dashboard Dilemma

  2. What We’ve Seen from NHS Governance Leaders

  3. The Three Jobs a Dashboard Should Do

  4. How Teams Are Making Dashboards Part of the Conversation

  5. What MEG Dashboards Help Surface

  6. Conclusion: Culture First, Then Tech

The Dashboard Dilemma 

Most governance leads want real-time visibility.
But visibility only helps when it:

  • Reaches the right people

  • Supports the right discussions

  • Surfaces what matters, not just what’s measurable

In several organisations, we’ve seen dashboards launched with energy, only to fade from view after initial rollout. Why? Because they weren’t integrated into how governance teams think, meet, or make decisions.

What We’ve Seen from NHS Governance Leaders

The Trusts we’ve learned the most from have something in common:

They didn’t just launch dashboards.
They built habits around them.

Some used domain-specific dashboards (e.g. Well-Led, Safe). Others developed role-specific views for Divisions, ward managers, or executive committees.

What mattered most?
The dashboards became part of the governance rhythm, not a side project.

The Three Jobs a Dashboard Should Do 

Based on what we’ve seen across partner Trusts, dashboards work best when they serve these three functions:

1. Surface signals, not noise

A good dashboard highlights what’s slipping, what’s overdue, or what’s out of pattern.
Clarity over complexity.

2. Prompt action

Every data point should have a clear implication: Who owns it? What’s the follow-up?
“Inform” isn’t enough. “Activate” is better.

3. Support assurance, not just reporting

Boards and committees need more than figures, they need confidence that risks are being seen, understood, and managed.

Dashboards must speak to governance visibility, not just operational tracking.

How Teams Are Making Dashboards Part of the Conversation 

Here are some patterns we’ve observed from Trusts embedding dashboards into governance culture:

✅ Dashboards Are Standing Agenda Items
In monthly Clinical Governance or Divisional meetings, live dashboards are reviewed alongside SIs and audit updates, not after the meeting as a slide.

🗂️ Governance Packs Pull from Dashboards, Not Spreadsheets
Several Trusts now use MEG dashboard exports as the base for their committee reports, Board Assurance Frameworks, or executive updates.

🧩 Local Teams Are Given Their Own Views
Ward or site-level dashboards help clinical teams see how their activity links to domain performance or inspection readiness.

🔄 Performance Reviews Reference Domain Dashboards
Safe, Well-Led, and Responsive data are presented not by exception, but as standard inputs to team reflection and performance cycles.

What MEG Dashboards Help Surface 

MEG dashboards were shaped by governance leaders who wanted clarity, not clutter.

🔹 CQC Domain Views
See audit coverage, incidents, risks and actions mapped to domain and Quality Statements

🔹 Live RAG Indicators
Highlight overdue actions, unverified learning, or gaps in assurance

🔹 Action Ownership
Track which service, team or individual is responsible and what’s been completed

🔹 Cross-System Integration
Link incidents to audits to policies, making learning and oversight easier to follow

Related Reading

Conclusion: Culture First, Then Tech 

The most effective governance dashboards aren’t the most advanced.
They’re the most used.

Embedding dashboards into governance culture doesn’t start with features. It starts with habits:

  • Reviewing dashboards together

  • Taking action from them

  • Reporting from them

  • Trusting them

When that happens, dashboards stop being reporting tools and become assurance systems.


Want to explore what dashboards could look like for your governance structure?

Book a MEG Dashboard Walkthrough and we’ll show you how NHS teams are using real-time views to support real-world decisions.

How to Embed Closed-Loop Learning in NHS Clinical Governance

Closed Loop Learning infographic

Introduction: Real Improvement Means Following Through

Across the NHS, governance leaders are united in one belief: learning matters most when it leads to change.

And under the Care Quality Commission’s updated Single Assessment Framework, that belief is now a clear expectation. The CQC wants to see not just that we review incidents, but that we close the loop, by turning insights into action, and actions into measurable improvement.

From our work with NHS Trusts, care providers, and governance teams, we’ve seen what this looks like in practice and where the challenges are.

This blog shares what we’ve learned from those organisations. It offers a practical roadmap to help you:

  • Make learning loops visible and trackable

  • Align assurance with CQC’s new expectations

  • Build a governance culture where improvement is consistently evidenced

Coming up:

  1. What Closed-Loop Learning Looks Like

  2. Why Even Strong Governance Teams Sometimes Struggle

  3. The 6-Stage Learning Loop in Practice

  4. How MEG Supports Teams in Closing the Loop

  5. Embedding the Loop: Tips from NHS Partners

  6. Conclusion + Next Steps

What Closed-Loop Learning Looks Like

At its simplest, a learning loop is the process of turning a safety or quality issue into a verified improvement in practice.

The loop can include:

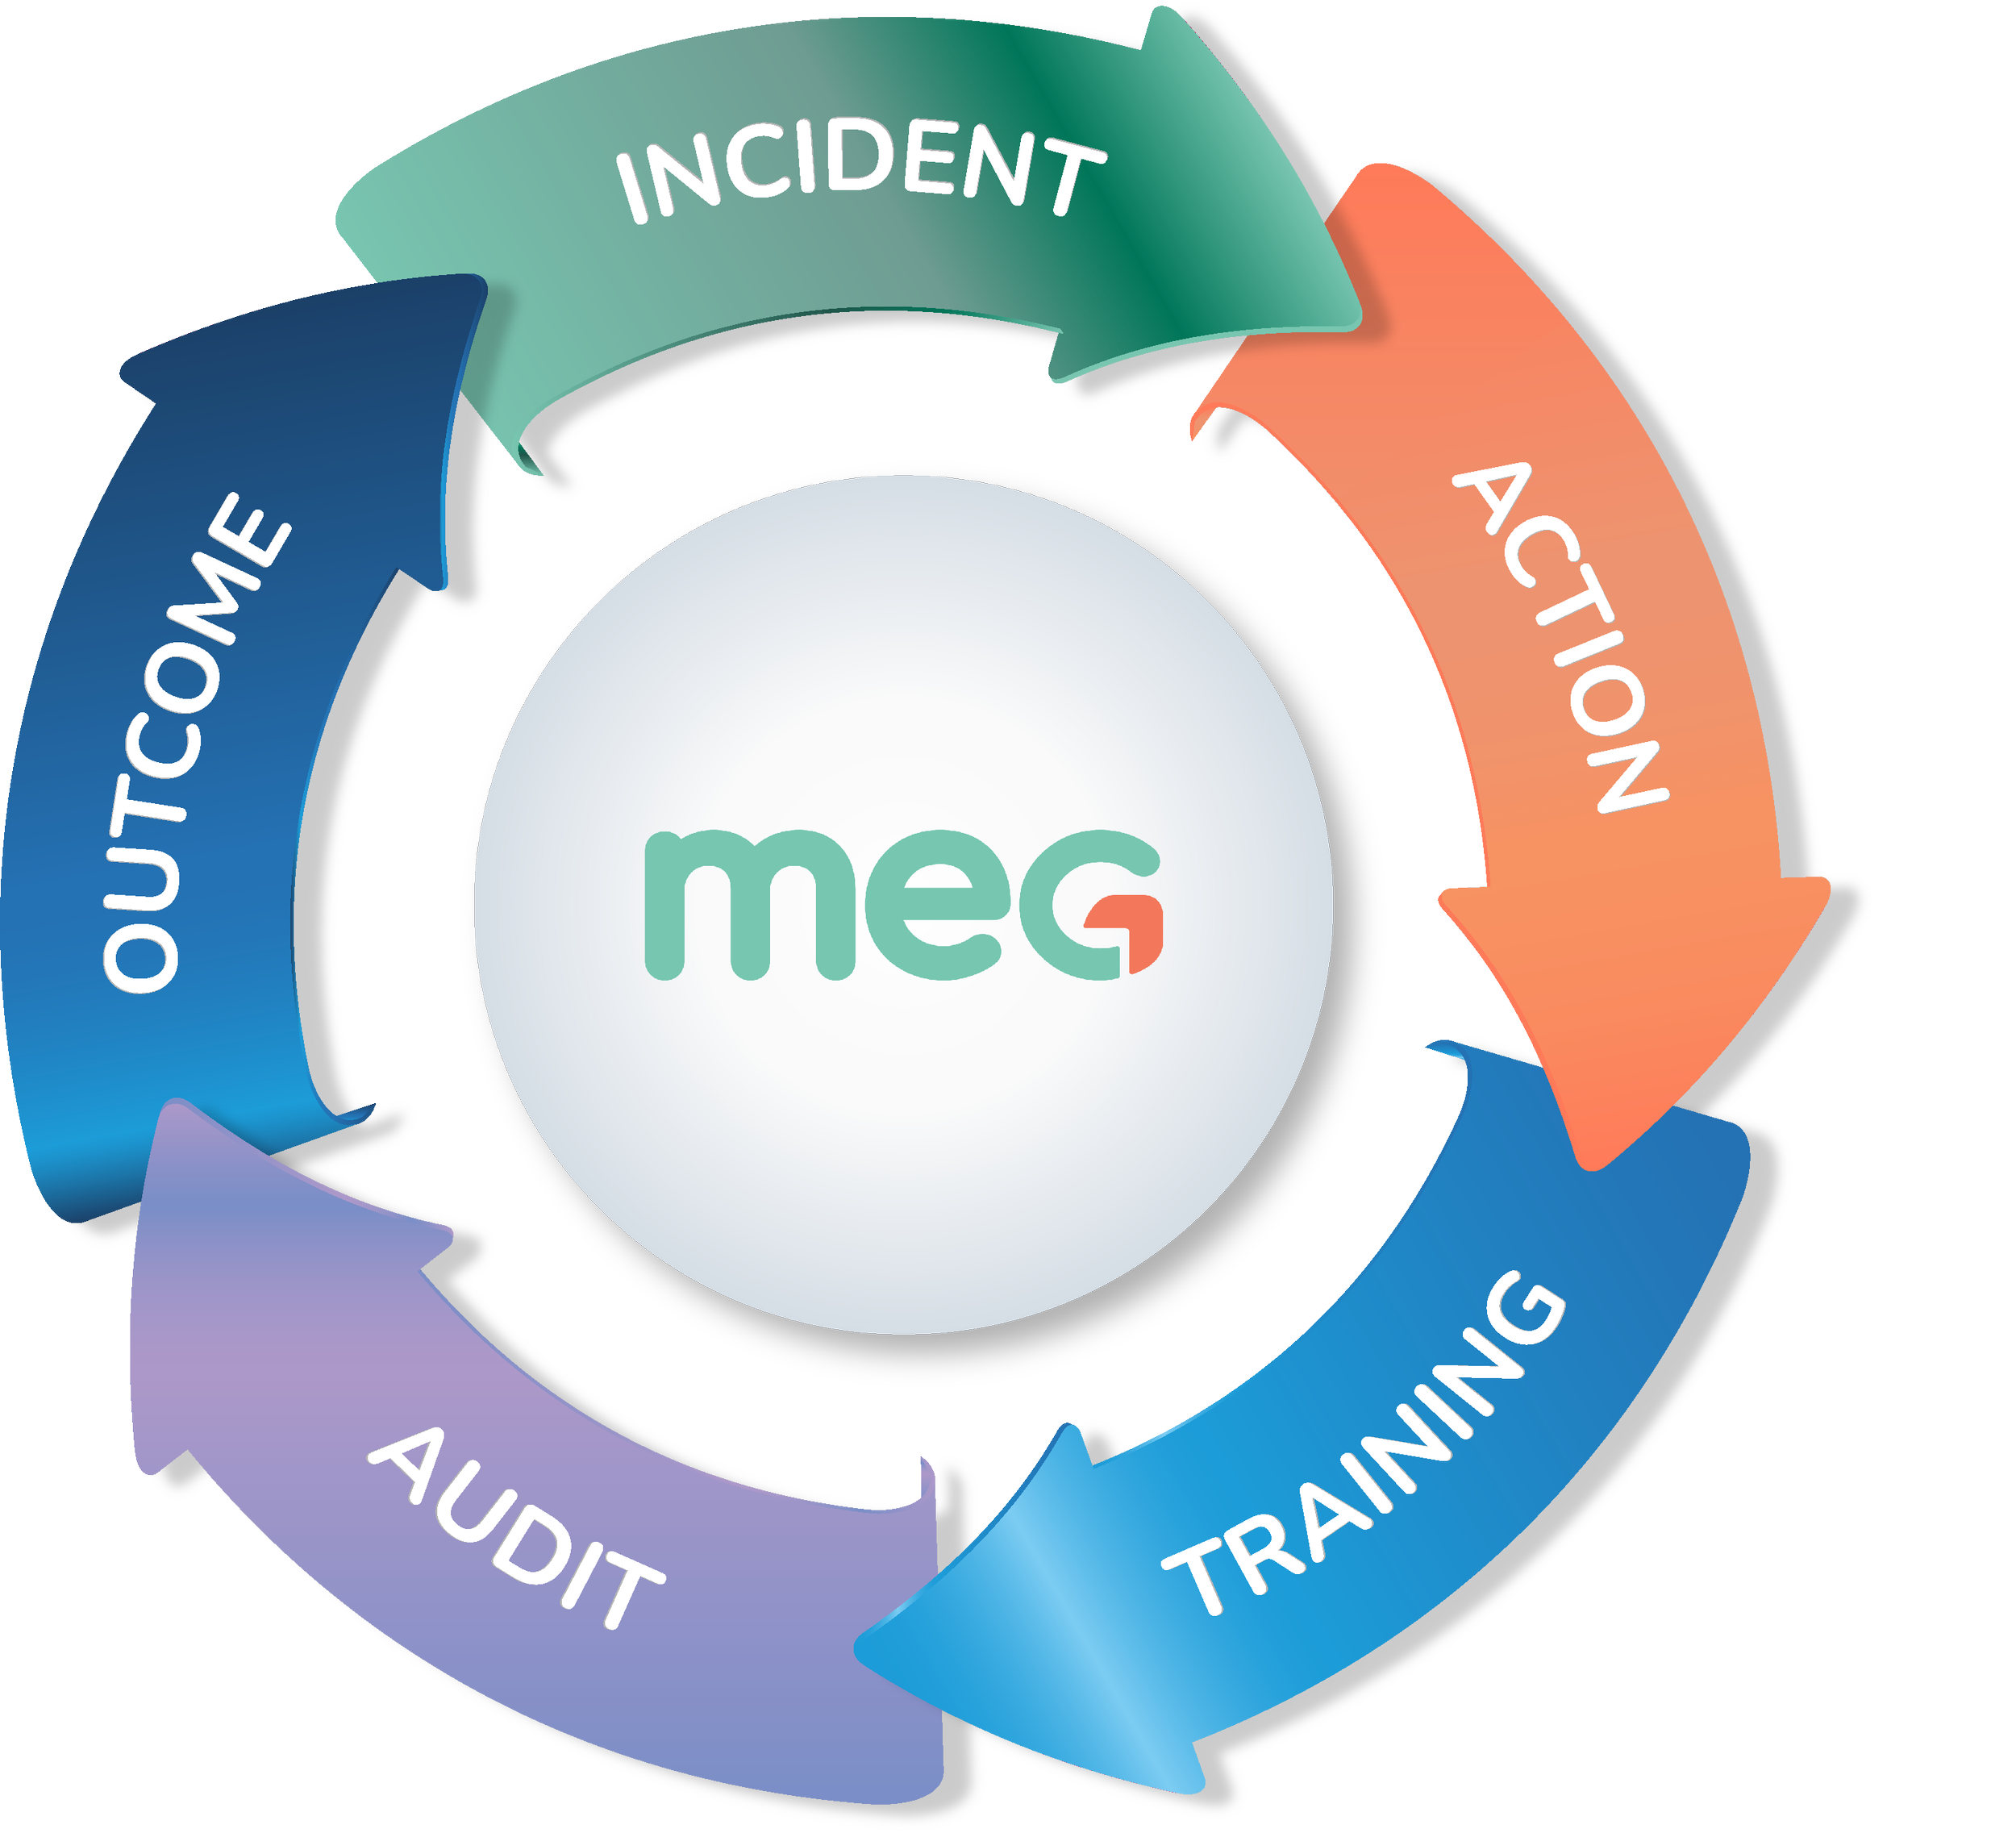
🚨 Incident or feedback → 📋 Action → 🎓 Training → 🔍 Audit → 📈 Outcome → ✅ Evidence of change

What progressive providers have shown us is that the loop isn’t about creating more paperwork. It’s about designing systems that make it easy to:

  • See where change is needed

  • Assign ownership

  • Track impact

And critically, show that improvement efforts are actually working.

Why Even Strong Governance Teams Sometimes Struggle

We’ve worked with teams who are deeply committed to improvement, but feel frustrated by the barriers in their way. Common themes include:

🔹 Data spread across systems
Incidents in Datix, audits in Excel, training on paper i.e. no single view.

🔹 Action plans that drift
Well-written action logs, but no way to track whether they were followed through.

🔹 Good intentions, missing evidence
Training is delivered, but no audit confirms whether practice changed.

These aren’t failures, they’re symptoms of governance systems that haven’t caught up with governance ambition.

The 6-Stage Learning Loop in Practice

Here’s the structure many of our NHS partners are using to close the loop more effectively:

1. 🚨 Trigger
Incident, complaint, audit failure, or staff concern

2. 📊 Analysis
PSIRF or thematic review to understand root causes

3. 📘 Action & Policy Review
Clear next steps, SOP updates, and named owners

4. 🧾 Credentialing / Training
Staff receive support and development, not just tasks

5. 🔍 Audit for Assurance
Check that changes are now part of everyday practice

6. 📈 Outcome Review & Loop Closure
Track the effect over time. Did things improve?

What we’ve learned: it’s not about complexity, it’s about clarity. When teams share a common loop (improvement) model, everyone knows what to do next.

How MEG Supports Teams in Closing the Loop 

MEG’s tools were shaped by feedback from quality and governance teams who wanted to simplify and strengthen the way they work.

Here’s how providers are using MEG to support the loop:

🔗 End-to-End Integration
Connects incidents, actions, training, policies, and audits

📊 Loop Dashboards
See live data on loop status, overdue steps, and domain performance

📋 Action Ownership
Assign tasks, set deadlines, and track progress visibly

🧠 Evidence Capture
Auto-generate reports showing how learning led to measurable change

One Trust used MEG to reduce their average ‘loop’ closure time by over 40% with MEG’s Action Planning tool.

Another created domain dashboards that now support Board-level assurance.

These aren’t just software features. They’re workflows that work because teams helped design them.

MEG's Action Planning tool

MEG’s Action Planning Tool - Demonstrate Open, In-Progress and Closed Tasks

Embedding the Loop: Tips from NHS Partners

The teams we’ve learned the most from have a few habits in common:

1. They standardise, but stay flexible
They adopt a core loop structure but let services adapt language or steps to their context.

2. They track loops, not just logs
It’s not just about counting incidents, it’s about showing improvement journeys.

3. They bring loop data into committees
Dashboards are shared in governance meetings, so learning becomes part of everyday assurance.

Related Reading

🎯 Conclusion + Next Steps

Embedding closed-loop learning doesn’t mean doing more.
It means creating clarity, so your governance efforts lead to meaningful, measurable change.

Across the providers we work with, we’ve seen that once the loop is visible, it becomes doable and once it’s tracked, it becomes culture.

🔄 Curious how your current learning loops stack up?
Book a call with the MEG team to see how loops could support even stronger assurance.

Aligning Audits with CQC Quality Statements

CQC audit tool

Audits That Do More Than Measure

When the Care Quality Commission introduced its Single Assessment Framework, governance teams across the NHS quickly recognised a shift, not in what audits were for, but in how they needed to work.

No longer was it about ticking the right boxes or ensuring every policy had been reviewed. Instead, audits were being reframed as evidence of lived experience, organisational learning, and impactful care.

This blog post reflects what we’ve seen—and learned—alongside NHS Trusts using MEG to make this shift. We’ll explore how teams are:

  • Reframing audits as part of a broader assurance story

  • Aligning templates to Quality Statements with minimal disruption

  • Using domain-based reporting to surface insight, not just activity

Coming up in this article:

  1. The Shift from KLOEs to Quality Statements

  2. What We’re Hearing from NHS Partners

  3. Three Ways Teams Are Adapting Their Audit Approach

  4. How MEG Supports Domain-Aligned Auditing

  5. Conclusion: From Coverage to Confidence

The Shift from KLOEs to Quality Statements

The transition from Key Lines of Enquiry (KLOEs) to 34 Quality Statements is more than cosmetic. It signals a shift in CQC’s expectations:

CQC Quality Statement audits

The transition from KLOEs to Quality Statements changed the context in which clinical audit evidence is considered. Instead of asking only whether a process is compliant, healthcare organisations increasingly need to demonstrate how assurance activity contributes to outcomes, learning and improvement.

For a full overview of the CQC assessment framework, read our guide to CQC assessments →

What We’re Hearing from NHS Partners 

Governance leads and quality managers we've worked with have shared some consistent themes:

🔸 “We don’t need more audits, we need better alignment.”
Many teams have strong audit coverage, but lack clarity on which Quality Statements are being evidenced (and where gaps exist).

🔸 “Our audits still reflect old structures.”
Some audit templates were designed around KLOEs or historical policies. They’re still useful but they don’t always reflect the new framework’s language or intent.

🔸 “We want to audit what matters not just what’s measurable.”
There’s a growing appetite to include cultural and experience-based domains (like Responsive and Caring) in audit programmes, not just procedural areas.

Three Ways Teams Are Adapting Their Audit Approach

1. Tagging, Not Rebuilding

Rather than redesign every audit from scratch, many teams are tagging existing audits to their relevant Quality Statements.

Example: An audit titled “Ward-Based Medicines Safety” is now tagged under “Safe: We learn when things go wrong.”

In MEG, these tags become filters for dashboards and reports.

2. Using Quality Statements to Identify Gaps

Some Trusts have used the CQC Statement list as a mapping tool, cross-referencing against audit coverage to see:

  • Where duplication exists

  • Where gaps are hidden

  • Which domains lack current audit data

This allows them to rationalise, not expand, their audit programme.

3. Making Audits Part of Domain Dashboards

By integrating audit results into MEG’s domain dashboards, teams can:

  • Track audit coverage across Safe, Effective, Well-Led, etc.

  • Monitor audit performance by service, location, or team

  • Include audits in regular governance reporting, not just inspection prep

How MEG's CQC Audit Tool Supports Domain-Aligned Clinical Auditing

MEG was designed to support audit frameworks that evolve with regulatory needs.

Key features include:

📂 Domain-Based Audit Templates
Easily tag audits to one or more Quality Statements

📊 Filterable Dashboards
Track coverage and performance by domain, service, or audit type

🔗 Link to Incidents and Actions
Surface learning and improvement journeys, from incident to audit follow-up

🧾 Auto-Generated Reports
Create board-ready views showing audit alignment across the organisation

Rather than managing clinical audits across spreadsheets and disconnected systems, MEG provides a configurable CQC auditing system where teams can manage audit activity, evidence, reporting and actions within one connected quality management platform.

CQC clinical audit

From CQC Audit Findings to Improvement

A clinical audit should demonstrate more than whether a standard was met on the day.

When MEG identifies a gap through a CQC-aligned audit, teams can create an improvement action directly from the finding, assign ownership, set deadlines and monitor progress through to completion.

By linking clinical audits, incidents, policies and action plans, governance teams can demonstrate the improvement journey behind the data, not simply audit activity.

Related Reading

Conclusion: From Coverage to Confidence 

The most effective audit programmes we’ve seen aren’t bigger.
They’re better aligned.

They reflect Quality Statements not just in name, but in outcome-focused evidence. And they make it easier for governance leads to demonstrate assurance, not just activity.

As more NHS teams embed this alignment into their tools and workflows, audits are becoming more than checks.

They’re becoming stories of progress and trust.

Curious how your audit programme aligns with CQC’s Quality Statements?
Book a call with the MEG team and get a domain-based snapshot in under 30 minutes.

Hospital Policy Management Software: Moving Beyond Document Storage

policy and procedure management in healthcare

Modern policy & document management for healthcare providers serious about care quality and accountability. 

MEG keeps your documents living, breathing and evolving.

Policies and procedures are fundamental to safe, consistent healthcare. But simply storing them digitally doesn't mean they are being effectively governed.

Hospitals need to know that policies are current, approved, accessible to the right staff and connected to the quality and compliance processes they support.

Hospital policy management software helps healthcare organisations move beyond document storage by providing greater control over the policy lifecycle, from review and approval through to distribution, version control and staff access.

MEG Docs was designed around this principle: policies should remain living, evolving parts of healthcare governance rather than static documents stored in folders.

Where Hospital Policy Management Can Break Down

Policy governance becomes difficult when healthcare organisations rely on disconnected folders, emails or systems that weren't designed around clinical workflows.

Review and approval processes may lack clear structure, while staff can struggle to find or understand the policy they need when they need it. Frontline accessibility can create further challenges, particularly where staff need information on mobile devices or in areas with limited connectivity.

Policies can also become disconnected from the processes they are intended to govern—including audits, incidents, risk management, training and quality improvement.

The result is a policy library that stores information without necessarily supporting active governance.

What Should Hospital Policy Management Software Do?

Effective healthcare policy and procedure software should help organisations manage the full lifecycle of a policy rather than simply provide somewhere to upload it.

Centralise Policies and Procedures

Policies, SOPs, clinical guidelines and other controlled documents should be managed through a centralised system where authorised staff can easily access the latest approved information.

Structure Reviews and Approvals

Policy review shouldn't depend on email chains. Structured workflows can support collaboration, approval, scheduled reviews and automated alerts, providing greater visibility into where each document sits within its lifecycle.

Maintain Version Control

When a policy changes, healthcare organisations need visibility over what changed, when it changed and who made the change.

Maintaining revision histories and ensuring current versions are distributed helps reduce the risk of staff relying on outdated information.

Make Policies Accessible to Frontline Staff

Policies only support care when staff can access them.

MEG Docs provides access across mobile and desktop devices, including support for environments with poor connectivity, helping put relevant policies, procedures and clinical guidance closer to the point of care.

Track Policy Engagement

Healthcare organisations may also need evidence that relevant staff have accessed and acknowledged important content.

Policy acknowledgement and reporting capabilities can provide greater visibility into staff engagement with new or updated information.

Help Staff Find the Right Policy Information Faster with AI

Healthcare policies and procedures can run to hundreds of pages. Finding the right document is only part of the challenge—staff may still need to locate a specific piece of information within it.

MEG's AI-powered document capabilities help authorised staff search, summarise and translate approved policies and documents, making it easier to find and understand relevant information.

Staff can use natural language questions to locate specific sections within lengthy documents rather than manually searching page by page. This can make approved policy information more accessible while helping healthcare teams spend less time searching through documentation.

MEG Docs vs. Other Document Management Systems on the Market

Purpose-built for healthcare. No workarounds required.

General document repositories can provide effective file storage, but healthcare policy governance requires more than somewhere to save a document.

MEG Docs is purpose-built for healthcare, combining document control with workflows designed around healthcare quality, governance and compliance.

Rather than managing policies separately from the processes they influence, organisations can connect documentation with audits, incidents, risks, actions and accreditation activity through the wider MEG platform.

MEG Docs vs General Document Management Systems

Healthcare Policy and Procedure Software Should Connect with Quality Management

Policy management is only one part of healthcare quality governance.

When an audit identifies a gap, an incident reveals a weakness in an existing procedure or an accreditation review requires supporting evidence, healthcare teams should be able to connect that activity with the relevant policies and improvement actions.

MEG connects Policy & Document Management with the wider QMS, including:

This means policies don't sit in isolation. They can be linked with the quality, risk and compliance processes they support, helping healthcare organisations move from document control towards continuous quality improvement.

MEG quality management software ecosystem

With MEG, policies don’t sit in isolation—they link directly to the quality, risk and compliance systems that power real governance.

MEG’s Document Management software played a key role in helping us achieve JCI accreditation across all three of our sites.

During the survey, our policies, forms, and SOPs were easy to access thanks to the intuitive, user-friendly layout—each folder was structured around JCI chapters, making navigation seamless.

I’m especially grateful to the MEG team for their patience, guidance, and consistent support throughout the entire process. Their platform and expertise were truly invaluable.”
— Helen Nolan Carty, former Head of Quality & Safety, Institute of Eye Surgery, Ireland

Frequently Asked Questions

Take Greater Control of Healthcare Policy Management

For more information or to schedule a demonstration of the MEG Docs Document/Policy Management system, please contact us at:

Enhancing Patient Data Management in Ireland: MEG and IPMS Integration

Timely access to accurate patient information is essential for effective care. To support this, we’ve launched a powerful new integration between MEG’s Quality, Risk & Compliance Management Software and the Integrated Patient Management System (IPMS). This new develoment aims to streamline how patient data will be managed across hospitals and clinics in Ireland.

In this post, we’ll break down how the integration works, why it matters, and the impact it’s expected to make in healthcare facilities across the country once fully rolled out.


Why This Integration Matters for Ireland’s Healthcare

The Irish Health Service Executive (HSE) is on a mission to modernise healthcare through its eHealth strategy. The MEG-IPMS integration aligns perfectly with this initiative, offering a unified approach to patient management that addresses three major pain points:

  • Inconsistent Patient Data: Manually updating records can lead to errors and outdated information.

  • Administrative Overload: Healthcare staff spend too much time on paperwork, reducing their ability to focus on patient care.

  • Delayed Decision-Making: Lack of real-time data can slow down critical treatment decisions, impacting patient outcomes.

The Solution

By combining the strengths of MEG’s Quality, Risk & Compliance Management System and IPMS, this integration enables seamless data exchange, automated updates, and real-time access to patient information, ensuring that healthcare providers have the tools they need to deliver the best possible care.

How It Will Work: Seamless, Secure Integration

The MEG-IPMS integration is designed to be simple, secure, and efficient. Here’s a look at how the process functions:

1. Secure Data Connection

A secure site-to-site VPN is set up between IPMS’s on-premise servers and MEG’s cloud environment. This ensures that all patient data is transmitted safely, in line with the highest standards of data protection.

2. Real-Time Data Syncing

Using HL7 standards (a set of guidelines for healthcare data exchange), patient admissions, transfers, and discharges are automatically updated across both systems, eliminating manual data entry and reducing the risk of errors.

3. User-Friendly Interface

Healthcare staff can then view synchronised patient data through MEG’s intuitive dashboard, simplifying clinical documentation and reporting.


Benefits for Every Role in Healthcare

This integration delivers tailored benefits across different roles in your facility:

✅ For Nurses and Physicians:

  • Faster Access to Patient Data: Make timely treatment decisions with up-to-date, accurate information.

  • Less Paperwork: Automated updates will free up more time for direct patient interaction.

✅ For Pharmacists:

  • Real-Time Medication Updates: Live access to admission and discharge info helps reduce medication errors.

  • Efficient Medication Management: Spend less time on manual entry, more on patient safety.

✅ For IT Teams:

  • Simple Integration and Maintenance: HL7 compatibility ensures smooth data exchange with existing systems.

  • Enhanced Security: VPN-secured and GDPR-compliant, guaranteeing the safety of patient data.

Addressing Common Questions

We understand that adopting new technology can raise concerns. Here's what to expect:

  1. Is patient data secure?
    Yes. The integration uses a secure VPN, adheres to HL7 standards, and ensures full GDPR compliance. All data is encrypted and protected.

  2. Will this disrupt our current workflows?
    No. The integration rollout is designed to be smooth and minimally disruptive, following a phased approach that typically takes less than 4 weeks. Full training and support will be provided.

  3. What support will be available after implementation?
    24/7 support will be available, including dedicated account managers and technical teams to resolve issues quickly.

The Future of Patient Care in Ireland

The MEG-IPMS integration is a key step toward a fully digitised healthcare system in Ireland. By reducing administrative burdens, improving data accuracy, and enhancing patient safety, this solution will empower healthcare providers to deliver higher-quality care with greater efficiency.


Take the Next Step: Be Among the First to Experience the Integration

Want to see how the MEG-IPMS integration can transform your workflows? Book a call with the team to learn more…

Document Management for Risk Control: Keeping Policies and Procedures Aligned

In the fast-paced world of healthcare, keeping policies and procedures aligned is a cornerstone of effective risk management. Hospital leaders face the critical challenge of ensuring that these documents are accessible, up-to-date, and actionable. Without proper document control, inconsistencies can lead to compliance gaps, inefficiencies, and increased risks. In this blog, we explore how MEG Docs supports healthcare organizations in managing policies and procedures seamlessly, offering practical examples and strategies for centralized document control. Improving processes, standardising them and integrating them with audit and risk management workflows reduces management waste.

The Importance of Accessible and Up-to-Date Policies

Policies and procedures are the backbone of healthcare operations, providing clear guidance for teams to ensure safety, compliance, and quality care. However, maintaining accessible and up-to-date documentation is often easier said than done. Here’s why it matters:

  1. Improved Compliance: Centralized and current policies help organisations meet regulatory standards, reducing the risk of fines or penalties.

  2. Streamlined Audits: Up-to-date documents facilitate smoother audits by providing accurate, readily available information.

  3. Enhanced Team Collaboration: When policies are accessible to all staff, it fosters alignment and reduces confusion in day-to-day operations.

For instance, a hospital facing recurring incidents of patient falls may discover outdated protocols contributing to the issue. Updating and sharing revised procedures ensures staff are equipped to prevent future incidents.

How MEG Docs Supports Document Control

MEG Docs is designed to address the complexities of document management in healthcare. Its features empower hospital leaders to:

  1. Centralise Document Storage: Keep all policies, procedures, and guidelines in a single, secure repository accessible to authorised personnel.

  2. Automate Version Control: Ensure staff always access the latest versions of critical documents, reducing errors caused by outdated information.

  3. Streamline Collaboration: Enable teams to review, edit, and approve documents in real-time, promoting accountability and efficiency.

  4. Integrate with Risk Management Workflows: Connect policy updates with incident data and audit findings to create a seamless feedback loop.

For example, a private clinic using MEG Docs integrated its incident reporting system with its document repository. When a medication error was reported, leadership swiftly updated the relevant policy and notified staff through the platform. This approach not only prevented recurrence but also strengthened compliance practices.

Practical Tips for Unified Document Repositories

To maximise the benefits of MEG Docs and other document management solutions, hospital leaders can implement the following strategies:

  • Conduct Regular Reviews: Schedule periodic audits of policies to ensure relevance and compliance.

  • Standardise Naming Conventions: Use consistent naming and categorisation for easy document retrieval.

  • Train Teams: Educate staff on accessing and using the document management system effectively.

  • Leverage Analytics: Monitor document usage and updates to identify gaps and improve processes.

These best practices create a robust framework for aligning policies and procedures, ultimately driving better risk control and operational efficiency.

Conclusion

In healthcare, effective document management is not just an administrative task—it’s a critical component of risk control and quality care. By ensuring that policies and procedures are accessible, up-to-date, and integrated into broader risk management workflows, hospital leaders can create a culture of accountability and continuous improvement. MEG Docs provides the tools to simplify document control, enabling organisations to focus on what matters most: delivering safe, high-quality care.

Ready to take your document management to the next level?
Find out how MEG Docs can help your healthcare organisation stay aligned and compliant while driving meaningful change.

From Reporting to Action: Turning Incident Data into Risk-Reducing Workflows

In today’s healthcare landscape, strong leadership is essential to drive safety, efficiency, and innovation. For hospital leaders, the ability to transform incident data into actionable workflows is a critical step in reducing risk and improving patient outcomes. Effective incident management isn’t just about collecting data—it’s about turning that data into meaningful actions that foster accountability, learning, and continuous improvement. This blog explores the leadership value of transforming incident reporting into risk-reducing workflows and offers strategies for building a culture of proactive problem-solving.

The Leadership Value of Actionable Workflows

As a leader, you understand that data is only as valuable as the actions it drives. An effective incident reporting system does more than capture incidents—it provides the foundation for risk-reducing workflows that address root causes and prevent repeat events. Here’s why this transformation matters:

  1. Root Cause Resolution: Actionable workflows ensure that incidents aren’t just logged and forgotten. They enable your team to dig deeper into the root causes, driving meaningful change and reducing the likelihood of recurrence.

  2. Data-Driven Decision-Making: A streamlined workflow system provides clear, organised data that informs leadership decisions, from resource allocation to policy updates.

  3. Use of the digital PDSA cycle in MEG: Use of Plan-Do-Study-Act for each process improvement cycle.

  4. Organisational Accountability: Leaders can set the tone for accountability by ensuring every incident follows a defined process, from reporting to resolution. This demonstrates a commitment to transparency and improvement.

For example, a hospital experiencing frequent medication errors can use incident data to identify trends, adjust training programs, and improve protocols. This not only enhances patient safety but also strengthens the trust of staff and patients in leadership.

Creating Repeatable Processes for Continuous Improvement

Consistency is key to achieving long-term improvement. By implementing repeatable workflows for incident management, leaders can ensure that every incident becomes a learning opportunity. Here’s how to build these processes:

  1. Standardisation: Develop standardised templates and workflows for incident reporting, investigation, and resolution. This ensures consistency across departments and sites.

  2. Feedback Loops: Establish mechanisms for sharing insights and lessons learned from incident reviews. For instance, monthly safety briefings can highlight trends and improvement areas, fostering a culture of learning.

  3. Follow-Up: Assign clear follow-up actions for each incident, whether it’s revising a policy, conducting training, or improving equipment. Leaders can track these actions to ensure accountability.

Hospitals that create a culture of repeatable processes see measurable improvements in patient safety and staff engagement. Employees feel empowered to report issues, knowing their input leads to actionable changes.

Fostering a Culture of Accountability and Improvement

Leadership sets the tone for organisational culture. By prioritising actionable workflows, hospital leaders can foster a culture of accountability and continuous improvement. Consider these strategies:

  1. Lead by Example: Demonstrate commitment by actively participating in incident reviews and championing changes based on incident data.

  2. Empower Teams: Provide teams with the tools and training needed to effectively report and address incidents. Empowerment leads to ownership and proactive problem-solving.

  3. Celebrate Successes: Recognize and reward teams that identify and resolve issues, reinforcing the value of incident reporting and workflow adherence.

When leadership emphasises accountability and improvement, it creates a ripple effect throughout the organisation. Staff become more engaged, patients receive safer care, and the hospital’s reputation as a leader in quality care is solidified.

Read our blog on turning incident reporting into lasting improvements

Conclusion

Transforming incident data into actionable workflows is a leadership opportunity to drive meaningful change in healthcare management. By addressing root causes, standardising processes, and fostering a culture of accountability, leaders can reduce risks and improve outcomes for patients and staff alike.

Ready to empower your organisation with actionable workflows?
Discover how MEG transforms incident reporting into risk-reducing workflows, equipping your team to make informed, impactful decisions.